Кибербезопасность
👉 от %username%
Подборка ресурсов по кибербезопасности
На русском 🇷🇺
Securitylab
последний пост 3 часа назад
Кроссовер за миллионы превратился в тыкву. Хакеры блокируют Li Auto и требуют выкуп
Кроссовер за миллионы превратился в тыкву. Хакеры блокируют Li Auto и требуют выкуп Кроссовер за миллионы превратился в тыкву. Хакеры блокируют Li Auto и требуют выкуп

Достаточно получить доступ к одной учётной записи, чтобы устроить владельцу настоящий мозговой штурм.

3 часа назад @ securitylab.ru
Заказ за 1 цент или без оплаты. Магазины на Drupal атакуют через дыру в оформлении покупок

Покупку можно было провести в обход защиты. Drupal подтвердил эксплуатацию критической дыры в Commerce Core

3 часа назад @ securitylab.ru
«Вояджер-1» замолчал на двое суток, а затем ожил сам. До рекордной дистанции осталось совсем немного

NASA сберегла последние ватты легендарного зонда. Скоро ответ с «Вояджера» будет идти двое суток

4 часа назад @ securitylab.ru
Китай предложил уменьшить ячейку DRAM на треть. Micron считает технологию тупиковой

Китайская CXMT проверила новые образцы памяти 4F². Началась инженерная гонка за плотность DRAM

4 часа назад @ securitylab.ru
10% российских ЦОДов уйдут в резерв, а при аварии сервисы смогут перенести за границу
10% российских ЦОДов уйдут в резерв, а при аварии сервисы смогут перенести за границу 10% российских ЦОДов уйдут в резерв, а при аварии сервисы смогут перенести за границу

Россия перестраивает резервирование дата-центров.

5 часов назад @ securitylab.ru
Два спутника NASA заглянули в магнитные «разрывы» возле Земли и обнаружили неожиданную закономерность

Космическая погода получила новый поворот.

5 часов назад @ securitylab.ru
Один лимит на ChatGPT и Codex. OpenAI меняет правила платных подписок с декабря

ChatGPT научится работать как агент без отдельного режима, но сложные задачи разделят общий лимит

5 часов назад @ securitylab.ru
Украли $2,7 млн, компенсировать пришлось $3,9 млн. Polymarket подсчитала цену заражённого скрипта

Строка стороннего JavaScript обошлась Polymarket почти в четыре миллиона долларов

6 часов назад @ securitylab.ru
Ссылка на чужой чат открывала доступ ко всем вашим перепискам ChatGPT. OpenAI закрыла дыру

Захват аккаунта без пароля и расширений. Исследователи взломали механизм публикации чатов ChatGPT

6 часов назад @ securitylab.ru
Ночной сбой Beget оказался кибератакой. Провайдер объявил форс-мажор
Ночной сбой Beget оказался кибератакой. Провайдер объявил форс-мажор Ночной сбой Beget оказался кибератакой. Провайдер объявил форс-мажор

DNS, почта и данные всё ещё восстанавливаются.

7 часов назад @ securitylab.ru
Сказки венского леса от Chainalysis: почему взлом главного трекера криптовалют пахнет позором

Под угрозой оказались данные пользователей платформы, среди которых сотрудники финансовых организаций и правоохранительных ведомств.

7 часов назад @ securitylab.ru
Хакеры разогрели морозильники до 50 °C. Супермаркеты Европы подсчитывают ущерб от кибератаки

После масштабного инцидента во Франции аналогичные проблемы возникли сразу в нескольких странах.

7 часов назад @ securitylab.ru
Рекламные щиты по всему миру внезапно начали показывать порно

Уличные экраны в нескольких странах одновременно оказались под чужим контролем.

8 часов назад @ securitylab.ru
HTTPS подделали за считаные минуты. Тысячи устройств продолжают верить фальшивым сертификатам

Cloudflare обнаружила подозрительные соединения даже после отзыва опасных ключей eMudhra.

8 часов назад @ securitylab.ru
VPN больше негде прятаться. В России начали отваливаться даже личные серверы
VPN больше негде прятаться. В России начали отваливаться даже личные серверы VPN больше негде прятаться. В России начали отваливаться даже личные серверы

Нейросеть или новый DPI?

8 часов назад @ securitylab.ru
Anti-Malware Anti-Malware
последний пост 6 часов назад
Красиво не значит верно: как собрать с ИИ презентацию, которой можно доверять
Красиво не значит верно: как собрать с ИИ презентацию, которой можно доверять Красиво не значит верно: как собрать с ИИ презентацию, которой можно доверять

Одно и то же число нужно и на основном слайде, и в summary, и в финальном выводе.

Гейты работают не с исходными данными, а с готовым артефактом: текстом, извлечённым из PDF, структурой слайдов и результатом рендера.

Общий смысл всех трёх групп один: отчёт выглядит готовым только после того, как прошёл гейты, а не после того, как отрисовался.

Теперь оно начинается не с вопроса «а всё ли вообще сошлось?», а с вопроса «правильно ли мы это интерпретируем?».

Где это не нужно и что не ловитЛегко прочитать всё предыдущее как «стройте CI для любой презентации».

6 часов назад @ anti-malware.ru
Тестовые фишинговые рассылки. Опыт крупных компаний
Тестовые фишинговые рассылки. Опыт крупных компаний Тестовые фишинговые рассылки. Опыт крупных компаний

Причём там обсуждалась реальная практика, в том числе и не вполне однозначный опыт.

В сочетании с языком Python и ИИ-моделью GigaChat от Сбера она позволяет создавать тестовые рассылки в электронной почте и мессенджерах.

Однако как для очень крупных, так и для совсем небольших компаний бесплатные продукты, скорее всего, не подойдут.

Одну из таких использовали и для организации обучения и тестирования сотрудников AM Live.

Это будет снижать их эффективность и, что хуже, создавать иллюзию защищённости и в итоге может приводить к возникновению инцидентов.

12 часов назад @ anti-malware.ru
Поиск следов атак (Compromise Assessment) в Linux-инфраструктуре: проект с нюансами
Поиск следов атак (Compromise Assessment) в Linux-инфраструктуре: проект с нюансами Поиск следов атак (Compromise Assessment) в Linux-инфраструктуре: проект с нюансами

Linux-инфраструктура особенно выделяется своей сложностью как для атакующих, так и для ИБ-специалистов, защищающих её.

Его нужно проводить по каждой системе отдельно, и в крупной инфраструктуре с сотнями серверов это кардинально меняет экономику проверки.

Что изучать и на что обращать вниманиеПервое, с чего стоит начинать на каждой системе, — список процессов и сетевых соединений.

Специфика закрепления в Linux-системахЗлоумышленники используют специальный набор техник для закрепления в Linux-инфраструктуре, и часть из них сложно обнаружить стандартными средствами.

Проверка переменной LD_PRELOAD в «/etc/ld.so.preload» и в окружении подозрительных процессов — обязательный пункт аудита, которы…

3 days, 6 hours назад @ anti-malware.ru
Вайбкодинг: антикризисное средство или источник проблем для ИТ-отрасли
Вайбкодинг: антикризисное средство или источник проблем для ИТ-отрасли Вайбкодинг: антикризисное средство или источник проблем для ИТ-отрасли

Как и в других отраслях, использование ИИ — один из путей снижения издержек и роста производительности труда.

К тому же для ИТ-отрасли, которая активно предлагает продукты с ИИ, не использовать такие средства самой было бы просто нелогично.

Владимир Лавров поделился опытом использования ИИ как для оптимизации бизнес-процессов, так и для ускорения разработки.

Поэтому нужно сначала выстроить методологию, платформу и инфраструктуру, затем определить задачи для ИИ и только после этого масштабировать автоматизацию.

Некоторые показатели внедрения ИИ в российских компанияхТакже использование ИИ создаёт большие риски в сфере подготовки кадров.

4 days, 5 hours назад @ anti-malware.ru
ЦОД со своей электростанцией: как новые правила меняют рынок
ЦОД со своей электростанцией: как новые правила меняют рынок ЦОД со своей электростанцией: как новые правила меняют рынок

Для ЦОДов такой механизм может ускорить запуск новых площадок, но не отменяет требования к непрерывности их работы.

Она также поможет ускорить ввод и не ждать строительства дополнительных электростанций и сетей.

При подключении по IV категории то оборудование, которое раньше служило аварийным резервом, берёт на себя роль второго потока обеспечения непрерывной работы объекта.

Надёжность всего дорожеКак именно IV категория надёжности в качестве сценария запуска ЦОДов повлияет на стоимость их сервисов, рынок пока только считает.

ВыводыIV категория надёжности не отменяет требования ЦОДа к непрерывности работы — она переносит часть задачи с внешней энергосистемы на самого оператора.

5 days, 4 hours назад @ anti-malware.ru
Российские СУБД 2026: рынок, регуляторика, миграция и прогнозы
Российские СУБД 2026: рынок, регуляторика, миграция и прогнозы Российские СУБД 2026: рынок, регуляторика, миграция и прогнозы

Выбор СУБД: универсальность против специализацииБудущее за универсальными СУБД, где есть и транзакционная, и аналитическая часть, или специализация останется?

Алексей Викулин согласился, что всё идёт от задачи, но большинство задач бизнеса соединяют потребность и в аналитике, и в транзакциях.

К SQL Server совместимость 98%, и к ним прилагаются компоненты инфраструктуры вроде Service Broker и SSRS (SQL Server Reporting Services).

Гарантию совместимости может дать только вендор прикладного решения, и идеальный вариант — когда вендоры СУБД и приложения работают в синергии.

Высокий порог входа требует от вендоров упрощения администрирования, развития инструментов управления СУБД и обучения спец…

5 days, 9 hours назад @ anti-malware.ru
От украденного пароля до остановки бизнеса: как защитить ретейл, когда периметра больше нет
От украденного пароля до остановки бизнеса: как защитить ретейл, когда периметра больше нет От украденного пароля до остановки бизнеса: как защитить ретейл, когда периметра больше нет

Ретейл — цель номер одинНа ретейл приходится около 25 % всех утечек данных в России и 33 % в мире: больше, чем на любую другую отрасль.

У среднего ретейлера сотни интеграций, многие из которых давно забыты и не обновляются.

Полномочия сервиса рассчитываются централизованно и передаются в самом токене, а не зашиваются в конфигурацию.

Готовое решение обходится бизнесу выгоднее самописной логики на фронте и при этом делает вход проще, а не сложнее.

Он значительно усиливает защиту данных, передаваемых между аутентификатором и сервером, от перехвата и служит для входа в почту, CRM-систему и корпоративный VPN.

5 days, 12 hours назад @ anti-malware.ru
Контроль сетевого доступа (NAC): от видимости устройств до управления и сегментации
Контроль сетевого доступа (NAC): от видимости устройств до управления и сегментации Контроль сетевого доступа (NAC): от видимости устройств до управления и сегментации

NAC перестал быть экзотикой: сегодня он определяет, кто и что попадает в корпоративную сеть, куда и на каких условиях.

Network Access Control перестал быть экзотикой и стал инструментом, который определяет, кто и что попадает в сеть, куда и на каких условиях.

Станислав Калабин согласился и добавил, что NAC всегда работает в комплексе с сетевым оборудованием и не может быть самостоятельным решением.

Появились разнородные устройства и несколько видов подключений, которые нужно контролировать, и без централизованного инструмента, который даёт картину и позволяет управлять, мониторить и реагировать, уже сложно.

Финальный опрос показал, планируют ли зрители усиливать контроль сетевого доступа по…

6 days, 11 hours назад @ anti-malware.ru
Баланс затрат и возможностей: что учесть при выборе системы защиты от утечек информации (DLP)
Баланс затрат и возможностей: что учесть при выборе системы защиты от утечек информации (DLP) Баланс затрат и возможностей: что учесть при выборе системы защиты от утечек информации (DLP)

ВведениеПри выборе DLP-системы бизнесу приходится искать баланс между возможностями защиты и затратами на её внедрение и эксплуатацию.

Поэтому при выборе DLP важно учитывать не только стоимость лицензии и количество контролируемых каналов, но и совместимость с ИТ-инфраструктурой, потребление ресурсов, отказоустойчивость и возможности автоматизации.

«СёрчИнформ КИБ» работает на серверах под управлением Windows и Linux, контролирует ПК на Windows, Linux и macOS.

Управлять КИБ на любой инфраструктуре можно из десктоп-приложения и в единой веб-консоли в браузере с любого устройства.

«СёрчИнформ КИБ» поддерживает разные типы блокировок — по действиям, по контексту и по контенту.

6 days, 14 hours назад @ anti-malware.ru
Обзор «Р7-Аналитики» 4.10, инструмента BI-аналитики
Обзор «Р7-Аналитики» 4.10, инструмента BI-аналитики Обзор «Р7-Аналитики» 4.10, инструмента BI-аналитики

Продукт относится к платформе «Р7-Офис», включённой в Реестр отечественного ПО, что позволяет применять его в госучреждениях и компаниях с госучастием.

Такой файл может включать около миллиона строк, однако «P7-Аналитика» позволяет обрабатывать огромные массивы данных без потери производительности.

Показатели выгружаются преимущественно из учётных и CRM-систем в виде таблиц данных и представляют собой числовые значения интересующей позиции учёта.

Загрузка показателейЧтобы загрузить табличный файл или подключить корпоративный источник данных (например, 1C или Битрикс24), нужно выбрать вкладку «Загрузка данных» в разделе «Настройки» главного меню программы.

Таким образом, пользователь может с…

1 week назад @ anti-malware.ru
Российские ИИ-агенты: переход от LLM к продвинутым цифровым помощникам
Российские ИИ-агенты: переход от LLM к продвинутым цифровым помощникам Российские ИИ-агенты: переход от LLM к продвинутым цифровым помощникам

Наглядная архитектура ИИ-агентаГотовые ИИ-агенты и ассистенты от российских разработчиковЧат-бот, который просто отвечает на вопросы, уже почти ушёл в прошлое.

Чтобы отличить ИИ-агента от обычного ИИ-ассистента и копилота, лучше всего оценивать уровень автономности, способность к планированию и степень участия человека:ИИ‑ассистент.

Крупные российские компании уже запустили продвинутых ИИ-агентов для собственных нужд.

Компания может проверить, какие данные и сервисы использовал агент при выполнении поручения и на чём основан результат.

Она позволяет создавать автономных ИИ-агентов и автоматизировать бизнес-процессы, поддерживая как российские модели YandexGPT и GigaChat, так и зарубежные LL…

1 week, 3 days назад @ anti-malware.ru
Тишина опаснее признания: как пауза в коммуникациях усиливает эффект кибератаки
Тишина опаснее признания: как пауза в коммуникациях усиливает эффект кибератаки Тишина опаснее признания: как пауза в коммуникациях усиливает эффект кибератаки

подозрений на киберинциденты, что в свою очередь уже на 40% больше, чем в прошлом году.

Например, во время сбоя в работе СДЭК в мае 2024 года хакерская группировка Head Mare публично заявила о взломе инфраструктуры компании и разместила скриншоты в подтверждение своих слов.

В результате вопросы возникли не только к надёжности сервиса, но и к тому, насколько точно компания описывает происходящее.

Тему подхватили СМИ, что в итоге сформировало негативное инфополе вокруг бренда.

После кибератаки у ритейлера возникли сбои в работе сайта, приложения и оборудования в магазинах, очереди на кассах и путаница с ценами.

1 week, 3 days назад @ anti-malware.ru
Российские операционные системы — 2026: зрелость, миграция и новые вызовы
Российские операционные системы — 2026: зрелость, миграция и новые вызовы Российские операционные системы — 2026: зрелость, миграция и новые вызовы

Денис Солоничкин отметил, что начались реальные внедрения: операционные системы больше не покупают «в стол», это видно по нагрузке на техподдержку и по продажам.

Для этого нужно провести внутренний аудит систем и софта, проверить ПО на предмет того, кросс-платформенное ли оно, и запланировать миграцию.

Денис Солоничкин пояснил, что РЕД СОФТ занимается общесистемным и инфраструктурным ПО и не идёт в те классы продуктов, где уже есть большое количество партнёров.

Инновации: агентские ОС и локальные моделиАнтон Пальгунов отметил движение в сторону веба и ИИ: пользователи всё чаще начинают с ИИ-ассистента, а не с поиска в браузере.

Одни считают, что зависимость неизбежна в любом варианте и важн…

1 week, 4 days назад @ anti-malware.ru
Агентный ИИ: как автономные агенты меняют разработку и администрирование
Агентный ИИ: как автономные агенты меняют разработку и администрирование Агентный ИИ: как автономные агенты меняют разработку и администрирование

Разбираемся, чем агент отличается от чат-бота и автоматизации, как его применяют в разработке и администрировании и какие риски возникают при доступе к корпоративным системам.

Он описывает, как агенты разных систем находят друг друга, обмениваются задачами и результатами и обрабатывают ошибки.

Поэтому к взаимодействию между агентами применяют те же принципы, что и к работе с инструментами: минимальные права, проверку входных и выходных данных, журналирование.

Как агенты меняют разработку ПОПри наличии разрешений агент работает с репозиторием, инструментами сборки и тестирования, закрывая многоэтапные задачи целиком.

При этом результат работы агента нужно проверять не только на ошибки, но и …

1 week, 5 days назад @ anti-malware.ru
Стратегия информационной безопасности на практике: с чего начать, как защищать
Стратегия информационной безопасности на практике: с чего начать, как защищать Стратегия информационной безопасности на практике: с чего начать, как защищать

Наталья Глинина отметила, что стратегия должна отвечать на вопрос, с какими бизнес-рисками работает компания, и обязательно связывать цели ИБ с целями бизнеса.

Евгений Акимов предложил смотреть на стратегию как на ожидание бизнеса от кибербезопасности: если бизнес ничего не ждёт, стратегия не нужна.

Евгений Акимов:«Прежде чем писать стратегию, нужно разобраться с целями бизнеса, а не с требованиями к кибербезопасности.

Елизавета Комарова:«Нужно учитывать, что угроза — это не то, что маячит на горизонте, а то, что происходит прямо сейчас.

Эксперты сошлись в том, что стратегия должна фокусироваться на критических процессах и их восстановлении, а не на перечне приобретаемых решений.

1 week, 6 days назад @ anti-malware.ru
Хабр: ИБ Хабр: ИБ
последний пост 1 час назад
[Перевод] Бэкдор с паролем 123456 и ключи в коде: как ИИ вскрывал «шифрованные» USB-накопители
[Перевод] Бэкдор с паролем 123456 и ключи в коде: как ИИ вскрывал «шифрованные» USB-накопители [Перевод] Бэкдор с паролем 123456 и ключи в коде: как ИИ вскрывал «шифрованные» USB-накопители

В последнее время я много и успешно реверсил и искал уязвимости вместе с ИИ, и мне захотелось проверить, как он справится с теми же задачами.

С одной стороны, меня удивило и даже немного встревожило, как быстро ИИ с этим справился.

"..0,ze.....% 00000030: 45 35 49 a4 58 1c 63 5b 4e e3 ee 0a 05 48 b3 56 E5I.X.c[N....H.V ... 00000250: 20 32 34 31 38 35 36 35 37 33 31 34 32 41 44 38 241856573142AD8 00000260: 38 32 30 36 43 45 31 42 46 38 33 35 46 41 38 46 8206CE1BF835FA8F 00000270: 37 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 7............... 00000280: 00 00 00 0e 6b 61 6b 61 65 6e 63 72 79 70 74 69 ....kakaencrypti 00000290: 6f 6e 08 42 6c 6f 77 46 69 73 68 on.BlowFishПервые восемь байт — …

1 час назад @ habr.com
Security Week 2645: уязвимость в UEFI при загрузке по сети
Security Week 2645: уязвимость в UEFI при загрузке по сети Security Week 2645: уязвимость в UEFI при загрузке по сети

Уязвимость с индексом CVE-2026-97631 приводит к повреждению памяти и в некоторых случаях может быть задействована для выполнения произвольного кода.

Непропатченный UEFI в системе, загружающейся по протоколу PXE, теоретически может быть атакован злоумышленником, который уже находится в локальной сети.

А это исследование разбирает обнаруженную экспертами «Лаборатории Касперского» уязвимость в IP-камерах Intelbras, приводящую к отказу в обслуживании.

Критическая уязвимость HTTP2Shell обнаружена в библиотеке Brotli, использующейся в том числе в Node.js.

Серьезная уязвимость закрыта в ПО TeamViewer.

2 часа назад @ habr.com
Почему UFW не спасает от Docker: анатомия сетевой подставы и что ищут боты в открытых портах БД
Почему UFW не спасает от Docker: анатомия сетевой подставы и что ищут боты в открытых портах БД Почему UFW не спасает от Docker: анатомия сетевой подставы и что ищут боты в открытых портах БД

В легковесных alpine‑образах этой дыры не было, а вот в сборках на базе debian в своё время поломали тысячи серверов.

И главное: при перезапуске контейнеров или самого демона Docker не трогает и не затирает то, что вы написали внутри DOCKER-USER .

А это значит, что весь входящий трафик к нему идёт не в транзитный FORWARD , а в стандартный INPUT — то есть попадает напрямую под действие обычных правил UFW.

Что поменялось в Docker 29+ с приходом нативного nftablesДолгое время Docker даже на свежих дистрибутивах управлял сетью через легаси‑прослойку iptables-nft .

До таблиц PREROUTING и DOCKER внутри гостевой ОС этот трафик физически не долетает, что бы там демон Докера ни накрутил в iptables .

7 часов назад @ habr.com
Кто заплатит, если ИИ-агент ошибётся: страхование ИИ-рисков в России и на Западе
Кто заплатит, если ИИ-агент ошибётся: страхование ИИ-рисков в России и на Западе Кто заплатит, если ИИ-агент ошибётся: страхование ИИ-рисков в России и на Западе

Я изучила российскую законодательную базу по ИИ в части страхования и сравнила её с тем, как страхование ИИ-рисков устроено за рубежом.

Национальная стратегия развития ИИ до 2030 года и Кодекс этики в сфере ИИ закрепляют принцип: ответственность должны нести человек или организация.

Концепция развития регулирования ИИ и робототехники до 2024 года прямо называла способы возмещения вреда от ИИ: страхование ответственности и компенсационные фонды.

Отчёт об инциденте AISI опубликовал в августе, а в октябре вышли подробные разборы причин от самого института и от Anthropic (см.

Обратите внимание и на логику aiSure: страховщик платит по данным о работе модели, а не по итогам спора о вине.

10 часов назад @ habr.com
Контейнер новый, код старый: почему инцидент вернулся через три месяца
Контейнер новый, код старый: почему инцидент вернулся через три месяца Контейнер новый, код старый: почему инцидент вернулся через три месяца

Инцидент вроде бы закрыли, отчитались, выдохнули — а через пару недель выясняется, что атакующий никуда не уходил.

Инцидент растянулся почти на три месяца, и повторная компрометация случилась уже после того, как были приняты меры.

Оба сайта работают под одним пользователем <пользователь> и в общей файловой системе.

Переразвёртывание не удаляет файлы из общей ФС и не проверяет cron и systemd — точки закрепления переживают «пересоздание» окружения.

И это, пожалуй, главный урок нашего инцидента: иногда самые очевидные меры реагирования лечат симптом, а не болезнь, и тогда злоумышленник возвращается — тихо, спустя недели, как будто никакой реакции и не было.

10 часов назад @ habr.com
Исповедь человека, который три года грабил маркетплейсы по промокодам для новорегов
Исповедь человека, который три года грабил маркетплейсы по промокодам для новорегов Исповедь человека, который три года грабил маркетплейсы по промокодам для новорегов

Застал золотую лихорадку, построил собственную ферму и вовремя спрыгнул с поезда, который на полном ходу летел в бетонную стену Уголовного кодекса.

Мы еще не знали, что на той стороне провода вместо сонных маркетологов к рулю уже встают безопасники.

Маркетинговые бюджеты урезали, а промокоды превратились в жалкую насмешку: «скидка 300 рублей при заказе от 3 500 рублей на товары без акций».

Физические сим-карты и прогретые аккаунты с историей заказов, которые стоят уже не 5 рублей, а по 150–300 рублей за штуку и живут ровно один заказ.

Столько же получает курьер, который привозил мне эти проклятые пакеты, только спит он спокойно, гуляет на свежем воздухе и не вздрагивает от звука тормозящего…

10 часов назад @ habr.com
Разработка на скорости машин: как найти (и починить) уязвимость в Linux и Ginux
Разработка на скорости машин: как найти (и починить) уязвимость в Linux и Ginux Разработка на скорости машин: как найти (и починить) уязвимость в Linux и Ginux

В README написано, что G в названии официально от GPT, а неофициально ещё и от Greg.

Ну а S в Ginux, как и в IoT, от Security.

Сначала модель угроз, затем три независимых прохода поиска: вслепую, от модели угроз и от истории CVE.

Пока мои отчёты превращались в PR для Ginux, Линус выпускал v7.4-rc1 с моим патчем.

А G, похоже, всё-таки от Greg: мой патч в Linux принимал один Грег, в Ginux — агенты другого.

11 часов назад @ habr.com
Архитектура в эпоху вероятности: почему наши старые чертежи больше не работают
Архитектура в эпоху вероятности: почему наши старые чертежи больше не работают Архитектура в эпоху вероятности: почему наши старые чертежи больше не работают

Мы живём в другой парадигме, где архитектура диктуется не просто рисками галлюцинаций LLM, а еще и технологическим суверенитетом.

Теперь она пишется не для ARB, а для машин.

Fitness functions описывают то, что не попадет в мастер, а токены делегирования — то, чего агент не сможет сделать сверх задачи пользователя.

Default-off, точки перехвата человеком, поведение при отказе, лимит токенов, exit path — каждый пункт очерчивает границу, а не маршрут.

Архитектор теперь проектирует не только поведение системы, но и место, где ответственность за дальнейшее решение переходит от машины к человеку.

11 часов назад @ habr.com
ИИ-хакеры против ИИ-безопасников: гонка вооружений и скорости в 2026
ИИ-хакеры против ИИ-безопасников: гонка вооружений и скорости в 2026 ИИ-хакеры против ИИ-безопасников: гонка вооружений и скорости в 2026

В самом инциденте (который в отчёте фигурирует как russian espionage) по данным Anthropic в планировании, разведке и атаках фигурировали более 20 организаций.

Злоумышленники использовали Claude для разработки и изменения инструментов, подготовки фишинговой инфраструктуры, сбора данных и управления отдельными этапами операций.

Но при организации испытания вкралась ошибка конфигурации, и на самом деле тестовая среда всё-таки могла подключаться к настоящим внешним сервисам.

Но пакет оказался в настоящем PyPI, и примерно за час его скачали и запустили на 15 реальных системах.

Что могло помочь и что делать для защиты: есть три защитных механизма, и они напрямую связаны с историей выше.

12 часов назад @ habr.com
Маскирование без дублей: перестановка вместо проверок на уникальность
Маскирование без дублей: перестановка вместо проверок на уникальность Маскирование без дублей: перестановка вместо проверок на уникальность

Весь конвейер «чтение → маскирование → запись» выдаёт на нашем стенде до 300 тысяч строк в секунду, и перестановка в нём не узкое место.

Переставлять целиком, а не по частям.

Подмножество сужается и на входе, и на выходе, поэтому отображение остаётся биекцией.

У FF1 десять раундов, и в каждом половины переводятся между строкой цифр и числом, а у нас восемь раундов из вызова AES и XOR.

Перестановка, заданная ключом, даёт уникальность и согласованность между таблицами без поиска по приёмнику и координации потоков.

12 часов назад @ habr.com
Ноутбук DevOps-инженера и $6,3 млрд: почему на безопасность нужно выделять время
Ноутбук DevOps-инженера и $6,3 млрд: почему на безопасность нужно выделять время Ноутбук DevOps-инженера и $6,3 млрд: почему на безопасность нужно выделять время

Мне интереснее другое: задачи по безопасности у нас месяцами лежат в бэклоге, а ноутбук инженера с доступом в прод остаётся самым удобным входом в компанию.

Почему это касается не только биржЦепочка «ноутбук инженера → контейнер в проде → действие, которое не откатить» есть почти в любой компании.

Когда инженер со своей машины ходит в прод, в логах это выглядит как обычная работа.

Пересмотреть, у кого есть доступ в прод и exec в поды критичных сервисов.

Договориться с ИБ о регулярной короткой встрече и о том, что новые проекты они видят на этапе дизайна.

12 часов назад @ habr.com
Искусственный интеллект меняет кибербезопасность. Что показывают исследования?
Искусственный интеллект меняет кибербезопасность. Что показывают исследования? Искусственный интеллект меняет кибербезопасность. Что показывают исследования?

Сам факт того, что ИИ способен обнаружить уязвимость, еще не означает, что неподготовленный человек сможет воспользоваться этой возможностью.

Особенность этих уязвимостей заключалась в том, что они находились не в конкретном пользовательском приложении, а непосредственно в интерпретаторе, причем в механизмах, которые участвуют в обработке огромного количества запросов.

Разработчики не могли выбрать решение, которое одновременно устраняло бы проблему и не создавало существенных побочных последствий.

PHP Foundation впоследствии прямо признала, что задержка была связана не только с технической сложностью, но и с недостатками организации работы и ограниченностью ресурсов команды.

Следовательно,…

13 часов назад @ habr.com
Взломщик стёр четыре строки. Хранилище их сохранило
Взломщик стёр четыре строки. Хранилище их сохранило Взломщик стёр четыре строки. Хранилище их сохранило

Как вы докажете проверяющему, что эти четыре строки пришли с web-1 в 07:28 и с тех пор их никто не трогал, вы в том числе?

Сначала строки взломщика попали в хранилище, потом файл подменили.

Если сборщик убить посреди работы, он продолжит с буфера, и ни одна строка не получит второй номер и не пропадёт.

Виртуальную машину сборщика подняли из снимка недельной давности: буфер вернулся в прошлое, хранилище нет, и новые строки получают номера, которые хранилище уже отдало другим.

Отдельная симуляция играет за нечестного владельца: придерживает записи и токены, подсовывает копии старых токенов, ставит звеньям время задним числом.

13 часов назад @ habr.com
Кража $6,3 млрд у Binance: анатомия крупнейшего взлома и его влияние на индекс Кассандры
Кража $6,3 млрд у Binance: анатомия крупнейшего взлома и его влияние на индекс Кассандры Кража $6,3 млрд у Binance: анатомия крупнейшего взлома и его влияние на индекс Кассандры

Косвенное подтверждение того, что работала та же рука, что и в прошлых кампаниях, дала блокчейн-аналитика TRM Labs.

Почему украденное - это военный бюджетДальше начинается часть, из-за которой событие попало в разбор недели индекса риска, а не в криптоновости.

В его власти немногое: не держать всё на одной площадке и не держать на бирже то, что не планируется продавать в ближайший месяц.

Не держать на бирже то, что не планируете продавать в ближайший месяц, и не концентрировать всё на одной площадке.

Не торговать на панике вокруг взлома: движение цены в такие дни - реакция на новость, а не на изменения в самой технологии.

15 часов назад @ habr.com
Как айтишникам живётся с информационной безопасностью на производстве ЕВРАЗа
Как айтишникам живётся с информационной безопасностью на производстве ЕВРАЗа Как айтишникам живётся с информационной безопасностью на производстве ЕВРАЗа

Сейчас в ЕВРАЗе довольно строгие регламенты по части информационной безопасности — всё, как принято в корпоративном секторе.

Как мы работаем с кейсами разработчиковВозвращаясь к вопросу, который мне задают на ИТ-конференциях: «Как вы заставили их так работать?».

А человек нам доказывал, что это не так, и мы не могли взломать, раз не знаем, как он устроен.

В частности, как контролировать информацию, которую люди передают в ИИ, и как быть с тем же вайбкодингом.

Мы постоянно думаем, как это лучше отслеживать с нашей стороны, — не запрещая всё на корню, но упреждая риски информационной безопасности.

19 часов назад @ habr.com
Хакер Хакер
последний пост 2 часа назад
Хакеры взломали Chainalysis с помощью ИИ-агентов
Хакеры взломали Chainalysis с помощью ИИ-агентов Хакеры взломали Chainalysis с помощью ИИ-агентов

В результате злоумышленники получили доступ к данным клиентов, включая их имена и email-адреса.

Представители Chainalysis пишут, что атакующие сумели проникнуть во внутренние системы компании и получили доступ к информации о пользователях платформы: ID, полным именам, email-адресам ролях пользователей в организациях.

При этом пока расследование не выявило признаков того, что хакеры могли получить доступ к содержимому расследований Chainalysis, учетным данным или сессионным токенам.

Параллельно в компании закрывают уязвимости, усиливают защиту и проводят масштабную проверку платформы вместе с внешними ИБ-экспертами.

В связи с утечкой данных в Chainalysis предупреждают клиентов о возможном фи…

2 часа назад @ xakep.ru
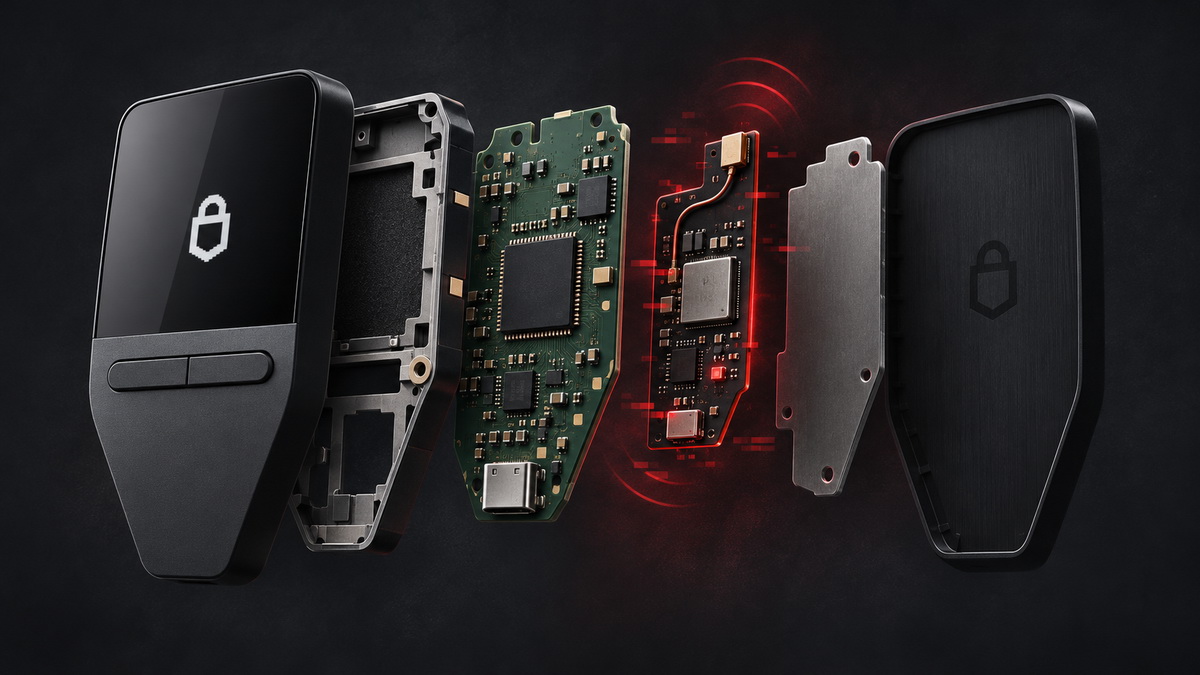
В аппаратных кошельках Trezor нашли вредоносные импланты
В аппаратных кошельках Trezor нашли вредоносные импланты В аппаратных кошельках Trezor нашли вредоносные импланты

Поэтому в Trezor рекомендуют создать новый кошелек с новой seed-фразой и перевести туда средства.

Также специалисты советуют не использовать и не настраивать новые устройства, приобретенные через CryptoBilis, и тем более не вводить в них seed-фразу.

При этом самостоятельно определять наличие импланта по весу или вскрывать кошелек в Trezor не рекомендуют.

В Trezor сообщают, что в их случае найденная плата выглядит похожей и, вероятно, работает по тому же принципу.

На фоне проводящегося расследования Ledger в Trezor прекратили продажи через CryptoBilis и исключили компанию из списка авторизованных продавцов еще в октябре 2026 года, а также сообщили, что пересмотрят всю глобальную сеть реселле…

4 часа назад @ xakep.ru
HTB MakeSense. Заставляем OCR распознать PHP-код и получаем root
HTB MakeSense. Заставляем OCR распознать PHP-код и получаем root HTB MakeSense. Заставляем OCR распознать PHP-код и получаем root

Справка: сканирование портовСка­ниро­вание пор­тов — стан­дар­тный пер­вый шаг при любой ата­ке.

На осно­ве этой информа­ции он выбира­ет сле­дующий шаг к получе­нию точ­ки вхо­да.

Улуч­шить резуль­таты его работы ты можешь при помощи такого скрип­та:#!/ bin/ bash ports = $( nmap -p- -- min- rate = 500 $1 | grep ^ [ 0 -9 ] | cut -d '/ ' -f 1 | tr ' ' ', ' | sed s/, $/ / ) nmap -p $ports -A $1Он дей­ству­ет в два эта­па.

На пер­вом выпол­няет­ся обыч­ное быс­трое ска­ниро­вание, на вто­ром — более тща­тель­ное, с исполь­зовани­ем встро­енных скрип­тов (опция -A ).

Под­робнее про работу с Nmap читай в статье «Nmap с самого начала.

6 часов назад @ xakep.ru
ФБР: Binance взломали северокорейские хакеры
ФБР: Binance взломали северокорейские хакеры ФБР: Binance взломали северокорейские хакеры

Еще на прошлой неделе блокчейн-аналитики писали, что инцидент связан с TraderTraitor, однако теперь эту атрибуцию официально подтвердили американские власти.

Специалисты ФБР, Секретной службы США и подразделения уголовных расследований Налоговой службы США заявили, что отслеживают движение похищенных у Binance активов.

В компании отмечают, что одна эта атака почти удвоила общую сумму криптовалюты, которую северокорейские хакеры похитили за последние годы.

Считается, что группировка TraderTraitor активна как минимум с 2020 года и специализируется на атаках на криптовалютные компании и их сотрудников.

В Binance подчеркивают, что потери не будут переложены на пользователей.

7 часов назад @ xakep.ru
Официальное расширение Claude Code на маркетплейсе Cursor подменили версией с бэкдором
Официальное расширение Claude Code на маркетплейсе Cursor подменили версией с бэкдором Официальное расширение Claude Code на маркетплейсе Cursor подменили версией с бэкдором

Через маркетплейс расширений для Cursor на протяжении почти 12 часов распространялась вредоносная версия официального расширения Anthropic Claude Code.

То есть пока остается неясным, каким образом злоумышленники получили возможность опубликовать вредоносное расширение под легитимным ID anthropic.claude-code на маркетплейсе Cursor.

Малварь запускалась автоматически при загрузке расширения и не требовала никаких действий со стороны пользователя.

Однако даже в этом случае расширение успевало добавить ключ злоумышленников в ~/.ssh/authorized_keys, зарепиться в системе и отправить собранные данные своим операторам.

Пользователям, которые установили или автоматически обновили Claude Code из Curso…

9 часов назад @ xakep.ru
Уязвимость SMS of Death может удаленно выводить из строя Android-смартфоны
Уязвимость SMS of Death может удаленно выводить из строя Android-смартфоны Уязвимость SMS of Death может удаленно выводить из строя Android-смартфоны

ИБ-исследователь Марк Бла (Mark Blah) опубликовал в открытом доступе PoC-эксплоит для недавно исправленной в Android уязвимости CVE-2026-58882, также получившей название SMS of Death.

По словам специалиста, эта уязвимость относится к классу zero-click DoS и может прервать уже идущий звонок, включая вызов экстренных служб.

Более того, Android обрабатывает вредоносное сообщение до того, как оно попадает во входящие, поэтому пользователь не видит само SMS и не понимает, что именно послужило причиной сбоя.

В результате атакующий может передать специально сформированное восьмибайтовое WAP Push-сообщение «01 06 88 80 80 80 00 BE».

Исследователь отмечает, что во время тестов 20 таких сообщений уво…

11 часов назад @ xakep.ru
Ежеквартальный «Хакер» #4 скоро отправится в печать
Ежеквартальный «Хакер» #4 скоро отправится в печать Ежеквартальный «Хакер» #4 скоро отправится в печать

Построить собственную сотовую сеть, разобраться в криптоалгоритме АНБ и написать хешкрекер на Go — эти и другие темы наши авторы разбирают на страницах четвертого ежеквартального номера «Хакера».

Передать номер в печать мы планируем в самое ближайшее время.

Среди статей:Собираем контейнер в Linux своими рукамиВскрываем криптоалгоритм АНБ СШАРазбираем, что нового в sqlmapПрокачиваем NmapИщем уязвимости в банковском приложенииИ еще много интересного!

В каждом из них собраны более 20 лучших статей, опубликованных на страницах «Хакера» в этом году.

— сравниваем скорость перебора хешей с разным софтом и железом, осваиваем сетевую разведку с Nmap и собираем PE-файл своими руками.

3 days, 2 hours назад @ xakep.ru
У Warp похитили логи работы ИИ-агентов и данные телеметрии пользователей
У Warp похитили логи работы ИИ-агентов и данные телеметрии пользователей У Warp похитили логи работы ИИ-агентов и данные телеметрии пользователей

Все статьи, PDF-архив, скидки и другие бонусыРазработчики Warp сообщили об атаке на стороннего подрядчика, связанного с инфраструктурой платформы.

В результате злоумышленники могли получить доступ к логам работы ИИ-агентов и пользовательской телеметрии.

Платформа объединяет терминал, редактор кода, инструменты для управления задачами и проверки работы агентов.

При этом в компании пока не уточняют, содержали ли скомпрометированные данные исходный код проектов, промпты, учетные данные или другую конфиденциальную информацию.

На прошлой неделе ее создатели предупредили об утечке API-ключей, которые пользователи сохраняли для работы со сторонними провайдерами.

3 days, 2 hours назад @ xakep.ru
На Polymarket внедрили скрипт для кражи криптовалюты
На Polymarket внедрили скрипт для кражи криптовалюты На Polymarket внедрили скрипт для кражи криптовалюты

Платформа Polymarket временно остановила торги после того, как хакеры скомпрометировали сторонний сервис DebugBear и распространили через него вредоносный JavaScript.

На время проведения расследования Polymarket сначала перешел в режим cancel-only, запретив новые сделки, а затем приостановил операции через релеи.

Анализ вредоносного скрипта показал, что тот проверял, авторизован ли посетитель в Polymarket, а при наличии активной сессии использовал штатные торговые функции платформы для несанкционированных операций.

Вредонос определял балансы кошельков и позиции пользователя на рынках прогнозов, после чего выбирал способ кражи криптовалюты в зависимости от метода аутентификации.

То есть инфр…

3 days, 4 hours назад @ xakep.ru
Минцифры готовит обязательную регистрацию IMEI для смартфонов, ввезенных для личного использования
Минцифры готовит обязательную регистрацию IMEI для смартфонов, ввезенных для личного использования Минцифры готовит обязательную регистрацию IMEI для смартфонов, ввезенных для личного использования

По информации РБК, в Минцифры работают над новыми правилами для смартфонов, ввезенных в Россию без таможенного оформления.

«При отказе от регистрации по истечении установленного срока такие устройства не будут обслуживаться в сетях», — пояснили в Минцифры.

Отмечается, что легальный ретейл эти изменения практически не затронут, так как IMEI официально ввезенных в Россию смартфонов будут попадать в централизованную базу автоматически.

Ранее сообщалось, что соответствующие требования могут начать действовать в 2027 году, а с 2028 года в мобильных сетях смогут работать только зарегистрированные телефоны.

Кроме того, за обязательную регистрацию устройств предлагалось взимать фиксированную плату,…

3 days, 7 hours назад @ xakep.ru
В камерах видеонаблюдения Intelbras обнаружили DoS-уязвимость
В камерах видеонаблюдения Intelbras обнаружили DoS-уязвимость В камерах видеонаблюдения Intelbras обнаружили DoS-уязвимость

Эксперты «Лаборатории Касперского» обнаружили DoS-уязвимость в IP-камерах Intelbras.

Из-за ошибки в механизме обновления прошивки неаутентифицированный злоумышленник мог добиться временного отключения камер.

Как объясняют исследователи, обычно для управления камерой требуется пройти аутентификацию, однако в случае Intelbras эндпоинт, отвечающий за обновление прошивки, не проверял наличие авторизованной сессии.

В результате устройство пропадало из сети, приложение Intelbras теряло с ним связь, а пользователь не мог просмотреть трансляцию и управлять камерой.

По данным представителей Intelbras, эта же версия прошивки совместима с моделями iMX C, iM4 C, iM5 SC, iME 360 C и iM7+ FC.

3 days, 9 hours назад @ xakep.ru
У криптобиржи Binance похитили рекордные 6,3 млрд долларов США
У криптобиржи Binance похитили рекордные 6,3 млрд долларов США У криптобиржи Binance похитили рекордные 6,3 млрд долларов США

Криптобиржа Binance расследует взлом, ущерб от которого в настоящий момент оценивается в 6,3 млрд долларов США.

Если сумма ущерба подтвердится, этот инцидент станет крупнейшим криптоограблением в истории: предыдущий рекорд принадлежал криптобирже Bybit, у которой северокорейские хакеры похитили около 1,5 млрд долларов США в феврале 2025 года.

Только в Ethereum хакеры получили активы примерно на 3,79 млрд долларов, а из биткоин-кошелька Binance похитили 18 270 BTC стоимостью около 1,47 млрд долларов США (по курсу на момент атаки).

В Binance рассчитывают полностью возобновить вывод средств в течение 48 часов.

По последней оценке экспертов самой Binance, суммарно удалось заморозить украденные …

3 days, 11 hours назад @ xakep.ru
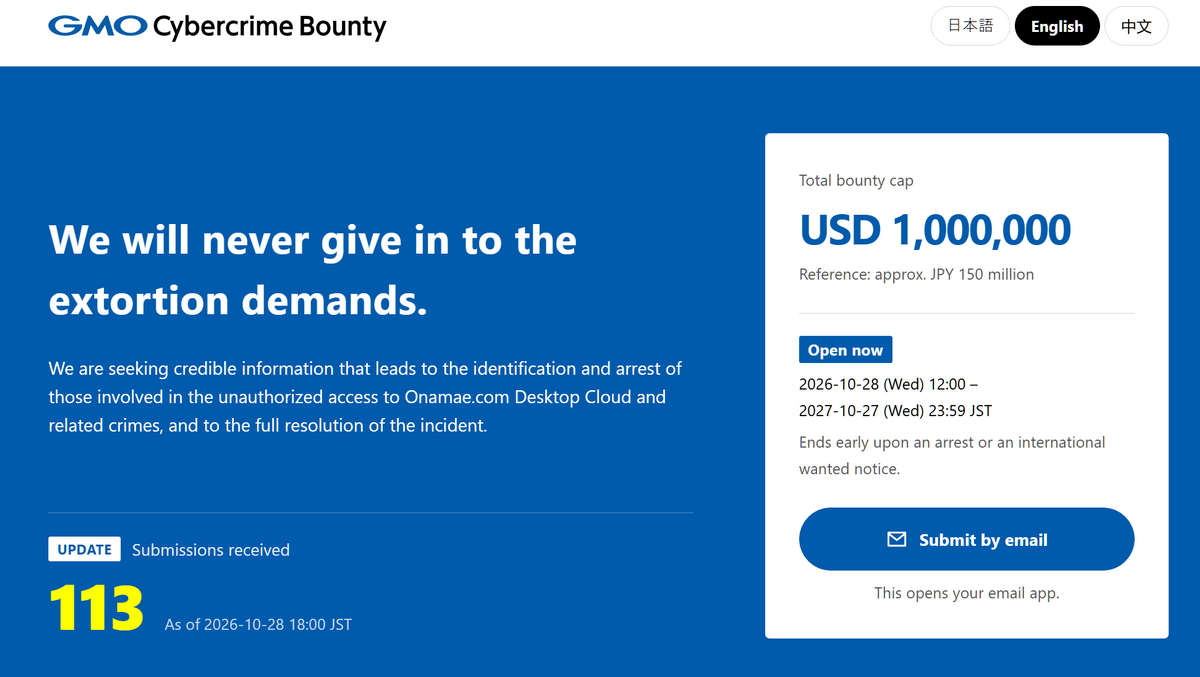
Компания GMO предлагает миллион долларов США за помощь в поимке хакеров
Компания GMO предлагает миллион долларов США за помощь в поимке хакеров Компания GMO предлагает миллион долларов США за помощь в поимке хакеров

Onamae.com — бренд компании GMO Internet, под которым работает один из крупнейших сервисов регистрации доменов в Японии.

Также в компании сообщили, что хакеры потребовали выкуп в размере 8 млрд иен, и представители GMO подчеркнули, что не станут платить злоумышленникам.

Позже в компании сообщили, что злоумышленники сдержали свое обещание и 27 октября действительно опубликовали данные, якобы принадлежащие GMO и ее клиентам.

В компании отказались платить выкуп хакерам, но пообещали компенсировать клиентам причиненный атакой ущерб.

Параллельно с этим в GMO объявили вознаграждение до миллиона долларов США за информацию, которая поможет поймать стоявших за атакой хакеров.

4 days, 2 hours назад @ xakep.ru
Discord позволит поисковикам индексировать сообщения на публичных серверах
Discord позволит поисковикам индексировать сообщения на публичных серверах Discord позволит поисковикам индексировать сообщения на публичных серверах

Представители Discord объявили, что сообщения из публичных сообществ скоро начнут появляться в поисковой выдаче Google и других поисковиков.

С середины декабря 2026 года на таких страницах начнут появляться отдельные сообщения из публичных каналов, которые смогут индексировать поисковики.

При этом старые сообщения, опубликованные до запуска функции, в поисковую выдачу не попадут, и на страницах не будут отображаться имена и аватары авторов.

Однако изменение настроек повлияет только на будущие сообщения, а уже опубликованную переписку можно будет убрать из открытого доступа, только удалив соответствующие сообщения из Discord.

Чтобы их сообщения могли появляться на Server Web Pages и индексир…

4 days, 4 hours назад @ xakep.ru
В кошельке Electrum исправили баг, позволяющий похищать криптовалюту
В кошельке Electrum исправили баг, позволяющий похищать криптовалюту В кошельке Electrum исправили баг, позволяющий похищать криптовалюту

Из-за уязвимости контролируемый хакером сервер мог подменять неподтвержденные транзакции в истории кошелька.

Если пользователь не замечал подмены и пытался ускорить перевод, повысив комиссию, Electrum создавал новую транзакцию с адресом атакующего вместо настоящего получателя.

Корень бага заключался в том, что Electrum работает как легкий клиент и получает данные о транзакциях через сеть Electrum-серверов, которые могут запускать сторонние операторы.

Также было недостаточно и самой подмены: кража происходила только в том случае, если жертва вручную увеличивала комиссию и подтверждала измененную транзакцию.

В Electrum 4.8.3, вышедшей 24 октября, разработчики добавили проверку подписей для не…

4 days, 7 hours назад @ xakep.ru
In English 🇺🇸
The Hacker News The Hacker News
последний пост 3 часа назад
⚡ Weekly Recap: Critical CVEs, Linux DDoS Botnet, Device-Code Phishing, Android Spyware and More
⚡ Weekly Recap: Critical CVEs, Linux DDoS Botnet, Device-Code Phishing, Android Spyware and More ⚡ Weekly Recap: Critical CVEs, Linux DDoS Botnet, Device-Code Phishing, Android Spyware and More

Silent Train is a relay infrastructure formed of compromised devices to hide the origin of its attacks.

Silent Train is a relay infrastructure formed of compromised devices to hide the origin of its attacks.

"Sales will switch to a preorder model until production of devices using the new key is complete, after which shipping will resume."

A total of at least 17,960 compromised devices have been identified, and about 7.6 million SMS messages were intercepted from victim devices.

A total of at least 17,960 compromised devices have been identified, and about 7.6 million SMS messages were intercepted from victim devices.

3 часа назад @ thehackernews.com
Google Disrupts 1.3 Million-Device Android Botnet, Says TV Box Maker Sold Criminal Access
Google Disrupts 1.3 Million-Device Android Botnet, Says TV Box Maker Sold Criminal Access Google Disrupts 1.3 Million-Device Android Botnet, Says TV Box Maker Sold Criminal Access

A botnet of more than 1.3 million Android devices, mostly TV set-top boxes, lost control of its servers in late October in a takedown led by Google.

Videostrong, based in Shenzhen, China, makes Android TV boxes and other devices under its own name and for other brands.

It banned the company, and any future subsidiaries or affiliates, from building or selling certified Android devices and from supplying software to other certified device makers.

Google has changed its review process and is improving its checks of the firmware on certified Android TV devices.

As of November 2, Videostrong's own website listed products it calls "Google Certified Android TV Box" and "Google Certified Android TV…

4 часа назад @ thehackernews.com
DarkBlinders Compromises Israeli Target and Iraqi Kurdish Government Cloud Environment
DarkBlinders Compromises Israeli Target and Iraqi Kurdish Government Cloud Environment DarkBlinders Compromises Israeli Target and Iraqi Kurdish Government Cloud Environment

The latest findings from Dream show that the threat actor continues to rely on social engineering, while combining both credential phishing and malware delivery.

]online/drive/file/d/1JpH3ySmJpvX6TyGnF7C-S8qYiaoxyC5OThe threat actor has also been observed setting decoy brand domains for a fake videoconferencing application called StarkMeet (stark-meet[.

The development is also a sign that the threat actor is trying out different methods for malware delivery, ranging from coding assessments to counterfeit software.

Dream said the DarkBlinders activity belongs to the same operational cluster as UNC5795 and Dust Specter, citing infrastructure and malware overlaps.

This is the last place we exp…

5 часов назад @ thehackernews.com
Critical Langflow Flaws Could Let Unauthenticated Attackers Run Code on Servers
Critical Langflow Flaws Could Let Unauthenticated Attackers Run Code on Servers Critical Langflow Flaws Could Let Unauthenticated Attackers Run Code on Servers

Two critical flaws in Langflow could let a remote attacker with no account bypass authentication or run arbitrary code, IBM said last week.

Six other Langflow flaws are listed there, most recently CVE-2026-9198, which was added in August.

Its author lists Langflow 1.5.0 through 1.11.4 as affected, a narrower range than IBM's.

On October 29, IBM also published CVE records for 29 other Langflow flaws and named versions 1.12.4 and 1.12.5 as their fixes.

One of them, CVE-2026-104339, could also let an attacker with no account run arbitrary code, and IBM rates it 9.8.

8 часов назад @ thehackernews.com
Is Your SOC Ready for AI Agents? A Maturity Check Before You Deploy
Is Your SOC Ready for AI Agents? A Maturity Check Before You Deploy Is Your SOC Ready for AI Agents? A Maturity Check Before You Deploy

AI SOC readiness has two parts: whether a SOC has the problems AI SOC agents are built for, and whether it has the data access, context, written standards and oversight rules that AI agents need to investigate alerts accurately in its environment.

Which SOCs benefit the most from AI SOC agentsThe SOCs that gain the most from AI SOC agents usually recognize several of the problems below, whether an outside provider works their alerts or their own analysts do.

Where AI agents fit on a SOC maturity modelProphet Security's SOC maturity model, the SOC Hierarchy of Needs, has five levels: alert management, detection coverage, threat awareness, proactive hunting and posture improvements.

An AI age…

8 часов назад @ thehackernews.com
Attackers Pose as IT Support on Microsoft Teams, Abuse AD CS to Steal Company Data
Attackers Pose as IT Support on Microsoft Teams, Abuse AD CS to Steal Company Data Attackers Pose as IT Support on Microsoft Teams, Abuse AD CS to Steal Company Data

Attackers posing as IT support on Microsoft Teams talked employees into giving them remote control of their PCs.

Microsoft said in a report that it investigated two such intrusions, one of which resulted in company data being copied to an external server.

With that kind of template, the requester can name the account the certificate will represent, so a low-privileged user can request one that stands in for a privileged account.

One privileged account, though, had been left out of the automatic response, so it stayed usable.

It also published three file hashes tied to the initial-access scripts:SHA-256 85b6c424117494d3056e88689dbc94c75e9afdb187a339714043aec0da109f17 (JavaScript initial-acce…

9 часов назад @ thehackernews.com
Government Linux Servers Targeted With SysGoRAT and Suspected AI-Generated Scripts
Government Linux Servers Targeted With SysGoRAT and Suspected AI-Generated Scripts Government Linux Servers Targeted With SysGoRAT and Suspected AI-Generated Scripts

Cybersecurity researchers have disclosed details of a cyber espionage campaign specifically targeting Linux infrastructure associated with government entities and state-affiliated infrastructure.

"The attackers attempted to dump sensitive databases and exfiltrate government mailboxes to access social media accounts."

The campaign employs a "versatile operational playbook," leveraging a combination of open-source tools, custom cross-platform backdoors, and web shells to maintain access.

The threat actor has also been observed using malicious PHP and shell scripts, likely generated using AI, to maintain persistence, perform reconnaissance, and exfiltrate data.

"They deployed a PHP script, nam…

9 часов назад @ thehackernews.com
New VOLTA Infostealer Uses Claude, Gemini, and Kimi AI to Rank Victims by Financial Value
New VOLTA Infostealer Uses Claude, Gemini, and Kimi AI to Rank Victims by Financial Value New VOLTA Infostealer Uses Claude, Gemini, and Kimi AI to Rank Victims by Financial Value

Cybersecurity researchers have discovered a new Windows infostealer malware called VOLTA-AUTODOXER (aka VOLTA) that makes use of a large language model (LLM) to rank a victim's stolen data by their monetization value.

"VOLTA builds a structured evidence bundle about the person behind the machine," Cisco Talos researcher Ryan Fetterman said.

The requests are defaulted to Anthropic's Claude Opus 4.6, failing which it falls back to Moonshot AI's Kimi K2 and Google's Gemini 2.5 Flash.

"If VOLTA is indeed a commoditized malware, then the AI dossier capability isn't something the author invented for their own operations," Talos said.

"VOLTA is a mature stealer with a late-stage AI layer added for…

14 часов назад @ thehackernews.com
CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key
CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key CVSS 10.0 LXD, MicroCloud Flaw Lets Attackers Impersonate Trusted Clients Without a Private Key

A critical flaw in Canonical's LXD and MicroCloud let an attacker log in as a trusted client without holding that client's private key.

The flaw, tracked as CVE-2026-112816, carries a maximum CVSS score of 10.0, and Canonical has released fixed versions of both products.

A standalone LXD server does not expose that API by default.

Canonical lists these fixed snap versions:Product Snap channel Fixed version LXD 6/stable 6.10.1 LXD 5.21/stable 5.21.9 LXD 5.0/stable 5.0.11 LXD 4.0/stable 4.0.15 MicroCloud 3/stable 3.4.1 MicroCloud 2/stable 2.1.5The bug did not start at Canonical.

On a snap install, run sudo snap refresh lxd and sudo snap refresh microcloud.

1 day, 11 hours назад @ thehackernews.com
Hackers Steal About $2.7 Million From Polymarket Traders via Hijacked DebugBear Script
Hackers Steal About $2.7 Million From Polymarket Traders via Hijacked DebugBear Script Hackers Steal About $2.7 Million From Polymarket Traders via Hijacked DebugBear Script

Malicious code on the website of prediction market Polymarket sold some signed-in traders' positions and moved their funds to the hackers on October 29.

Researchers at Hudson Rock downloaded the malicious file on October 29 from the address Polymarket's site used to load the DebugBear script.

They also found a change in Polymarket's site code that removed the DebugBear script.

Each DebugBear customer loads its own copy of the script, and the file that was swapped was Polymarket's.

For accounts that sign in with their own crypto wallet, it moves the trader's positions straight to the hackers' wallet.

1 day, 12 hours назад @ thehackernews.com
NetamLoader Malware Targets Government Windows 10 Systems in Asia via .NET Injection
NetamLoader Malware Targets Government Windows 10 Systems in Asia via .NET Injection NetamLoader Malware Targets Government Windows 10 Systems in Asia via .NET Injection

AppDomainManager injection is an adversarial technique used to load arbitrary payloads by hijacking .NET Framework's AppDomainManager mechanism when a .NET application starts.

"Resources.resx" contains "multiple layers" of encoded, compressed, or encrypted payloads, such as XAML files, .NET assemblies, and JSON data, which are decoded and loaded by the component before it.

XAML‑2 initializes the second stage of the attack chain by loading two compressed and Base64‑encoded XAML files: XAML-2-1 and XAML-2-2 .

XAML-3 , the XAML payload that runs within "dllhost.exe" and is designed to decode, decompress, and load .NET 2 Plugin.

, the XAML payload that runs within "dllhost.exe" and is designed …

1 day, 13 hours назад @ thehackernews.com
FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist
FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist FBI Links North Korea's TraderTraitor to Record $6.43 Billion Binance Crypto Heist

The FBI, along with the U.S. Secret Service (USSS) and the Internal Revenue Service Criminal Investigation (IRS-CI), said it observed the threat actor converting stolen assets primarily into Ethereum (ETH).

The agency has also provided a list of wallet addresses that the attackers are said to be using to launder the stolen assets.

The haul eclipses the $1.46 billion plundered from Bybit in February 2025, making it the largest cryptocurrency theft in history.

Of the $6.43 billion stolen by TraderTraitor, $2.85 billion of the assets have been frozen on-chain by Tether, Circle, Ripple, Arbitrum, and Optimism.

"Within this short time frame, Jade Sleet conducted similar job-themed targeting usin…

1 day, 13 hours назад @ thehackernews.com
Chainalysis Confirms Intrusion Into Internal Tools and Exposure of Customer Identity Data
Chainalysis Confirms Intrusion Into Internal Tools and Exposure of Customer Identity Data Chainalysis Confirms Intrusion Into Internal Tools and Exposure of Customer Identity Data

American blockchain analysis firm Chainalysis said it was the target of a cybersecurity incident in which an external actor accessed non-sensitive customer data.

However, the company noted that the breach did not result in unauthorized access to its investigation content, authentication credentials, or session tokens.

"This month, Chainalysis detected an external actor using offensive agentic techniques to gain unauthorized access to Chainalysis systems and internal tools," Chainalysis said Friday.

"AI mainly improves established attacks by making them faster, more personalized, and easier to scale," Abnormal AI said.

"Agentic intrusion chains and prompt injection are more distinct because …

2 days, 8 hours назад @ thehackernews.com
Attackers Chain Three Ivanti Connect Secure Flaws to Gain Unauthenticated Root Access
Attackers Chain Three Ivanti Connect Secure Flaws to Gain Unauthenticated Root Access Attackers Chain Three Ivanti Connect Secure Flaws to Gain Unauthenticated Root Access

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Ivanti Connect Secure (ICS) to its Known Exploited Vulnerabilities (KEV) catalog, following active exploitation in the wild.

The vulnerabilities are listed below -CVE-2026-111357 (CVSS score: 8.8) - A missing authentication for a critical function vulnerability that could allow a local authenticated attacker to escalate their privileges.

(CVSS score: 8.8) - A missing authentication for a critical function vulnerability that could allow a local authenticated attacker to escalate their privileges.

"This exploit chain combined an authentication bypass, a remote code execution (RCE), an…

2 days, 11 hours назад @ thehackernews.com
A Shared ChatGPT Link Could Run Attacker Code in Your Session and Read Private Chats
A Shared ChatGPT Link Could Run Attacker Code in Your Session and Read Private Chats A Shared ChatGPT Link Could Run Attacker Code in Your Session and Read Private Chats

A malicious ChatGPT share link could run an attacker's code in the logged-in session of anyone who opened it, allowing them to read their private conversations, researchers at the security firm Parameter showed.

It could be sent the same way as any real shared chat: by email, as a chat message, as a support ticket, or as a social post.

What the Attacker Could DoOnce the link opened, the attacker's code ran inside the victim's signed-in session with the same access as the real ChatGPT site.

Because that page can hold any code, ChatGPT runs it in a locked-down frame on a separate web address, where it cannot read the main ChatGPT page around it.

The shared chat also contained an interactive g…

2 days, 14 hours назад @ thehackernews.com
threatpost threatpost
последний пост None
DarkReading
последний пост None
WeLiveSecurity
последний пост 3 days, 5 hours назад
This month in security with Tony Anscombe – October 2026 edition
This month in security with Tony Anscombe – October 2026 edition This month in security with Tony Anscombe – October 2026 edition

The PHP2Shell disclosure and other major cybersecurity news this month brought into relief the need for well-thought-out cyber-readiness plansWith October coming to a close, ESET Chief Security Evangelist Tony Anscombe reviews some of the top cybersecurity stories that made the news over the month.

At the same time, he offers insights that the latest wave of incidents hold for your company's, or your own, cyber-defenses.

A data breach at Denmark’s Central Population Register (CPR) has exposed the personal information of 8.8 million people.

What are the lessons that businesses should take away from the latest cybersecurity news?

Watch Tony's video to find out, and be sure to check out the Se…

3 days, 5 hours назад @ welivesecurity.com
Amatera: How the prolific infostealer works and spreads
Amatera: How the prolific infostealer works and spreads Amatera: How the prolific infostealer works and spreads

Amatera – which topped ESET’s infostealer detections in Latin America in the first half of 2026 but targets victims worldwide – shows what this professionalization looks like in practice.

Detected by ESET products as Win/PSW.Amatera, Amatera is a Windows infostealer written in C++ that was first observed in 2024.

Amatera has spread via compromised websites, search engine ads, targeted emails, fake documents, SVG files, and ClickFix via fake CAPTCHAs.

In Latin America, Amatera topped ESET’s infostealer detections in the first half of 2026, ahead of Formbook, Vidar, Lumma Stealer, SnakeStealer, and Rhadamanthys.

A developer maintains the product, and other actors distribute it via compromised…

4 days, 12 hours назад @ welivesecurity.com
Lessons from Cybersecurity Black Week
Lessons from Cybersecurity Black Week Lessons from Cybersecurity Black Week

In the age of AI, all of this was reported within a single “Cybersecurity Black Week,” an exceptionally eventful seven-day period amid an already turbulent Black October.

The name refers to two memory-safety vulnerabilities in PHP core, CVE-2026-109618 and CVE-2026-109619, affecting PHP versions 5.4 through 8.5.11.

The same decoder is compiled into the Python Brotli and brotlicffi packages as well as into other HTTP software, which led researchers to rename the issue HTTP2Shell.

Cutting through the noiseCybersecurity Black Week showed that a severity score rarely tells the whole story.

For the leaked kernel flaws, that window opened before any fix existed, and for end-of-life PHP versions, …

5 days, 9 hours назад @ welivesecurity.com
ESET APT Activity Report Q2 2026–Q3 2026
ESET APT Activity Report Q2 2026–Q3 2026 ESET APT Activity Report Q2 2026–Q3 2026

ESET APT Activity Report Q2 2026–Q2 2026 summarizes notable activities of selected advanced persistent threat (APT) groups documented by ESET researchers between April and September 2026.

They represent only a subset of the cybersecurity intelligence made available to customers of ESET Threat Intelligence APT Reports.

In Southeast Asia and Oceania, China-aligned threat actors ran campaigns that appear to support Chinese law enforcement efforts against organized crime in the region.

Finally, we identified several cases of APT groups using AI and large language models (LLMs) at various stages of their operations.

Threat actors used AI primarily to accelerate tasks that would otherwise require…

5 days, 10 hours назад @ welivesecurity.com
PHP2Shell: What to know about two critical PHP flaws
PHP2Shell: What to know about two critical PHP flaws PHP2Shell: What to know about two critical PHP flaws

The news prompted security advisories from government agencies and sent website owners scrambling to apply the patches, with some sites even going offline as a precaution.

This is because on an unpatched server, an attacker can exploit the vulnerabilities to run their own code without logging in.

As three out of four websites globally are estimated to use PHP in some capacity, its ubiquity helps create an environment ripe for abuse; indeed, initial attempts to exploit the flaws – discovered by AI and dubbed PHP2Shell – weren't long in coming.

Here's what to know about CVE-2026-109618 and CVE-2026-109619, as well as what website owners and IT teams should do to stay safe – all in a little mo…

1 week назад @ welivesecurity.com
MythicRatatoskr: An Yggdrasil-enabled backdoor deployed in a UAC-0099-Sandworm collaboration
MythicRatatoskr: An Yggdrasil-enabled backdoor deployed in a UAC-0099-Sandworm collaboration MythicRatatoskr: An Yggdrasil-enabled backdoor deployed in a UAC-0099-Sandworm collaboration

The following day, at 09:28, a new binary was delivered to the machine: the MythicRatatoskr backdoor.

This blogpost focuses primarily on the analysis of the MythicRatatoskr backdoor, the Yggdrasil network that hosts its C&C server, and the accompanying SOCKS5 server.

Given the backdoor’s role as a messenger scurrying through the Yggdrasil network, we decided to name the backdoor MythicRatatoskr.

MythicRatatoskr main configurationThe MythicRatatoskr configuration is stored in a file at a hardcoded path.

NetworkIP Domain Hosting provider First seen Details b479:2771:8df4:b5e b:d007:63b0[:]2838 N/A N/A 2025‑07‑17 MythicRatatoskr C&C server within the Yggdrasil network.

1 week, 4 days назад @ welivesecurity.com
Is the ad a scam? How to tell before you click
Is the ad a scam? How to tell before you click Is the ad a scam? How to tell before you click

In some cases, the scam ad may take you to a fake e-commerce site which covertly harvests your card details.

What happens if I’ve fallen victim to a scam ad?

Scam ads are getting easier to generate thanks to AI, and can look increasingly professional, even including video content.

Can I get my money back if I paid through a scam ad?

What should I do if I’ve fallen victim to a scam ad?

1 week, 6 days назад @ welivesecurity.com
Inbox flooded with sign-up messages? Email bombing explained
Inbox flooded with sign-up messages? Email bombing explained Inbox flooded with sign-up messages? Email bombing explained

This is email bombing.

What is email bombing?

Sometimes called “form bombing,” “list bombing” or “subscription bombing,” email bombing attacks usually follow the same pattern.

There’s no silver bullet to prevent email bombing.

Has my email account been hacked if it’s full of sign-up emails?

2 weeks, 3 days назад @ welivesecurity.com
Medicare scam calls, texts and ads: What to watch for this Open Enrollment
Medicare scam calls, texts and ads: What to watch for this Open Enrollment Medicare scam calls, texts and ads: What to watch for this Open Enrollment

Open Enrollment is peak season for Medicare fraud – here’s how to tell real outreach from fakes and keep your details safeScammers love a pretext.

And with Medicare Open Enrollment, they have a perfect opportunity to exploit victim expectations, masking their fraud under the cover of legitimate activity.

Work through the following steps:Call or contact Medicare at Medicare.gov or 800-633-4227 to report the incident.

So slow down this Open Enrollment season and verify every request for personal and medical details.

Frequently Asked Questions (FAQs)When is Medicare Open Enrollment?

2 weeks, 5 days назад @ welivesecurity.com
What to do when a data breach notice doesn't say much
What to do when a data breach notice doesn't say much What to do when a data breach notice doesn't say much

Data breach notifications are telling victims less than ever.

As the volume of data breach incidents increases, there’s a growing chance that you’ll be caught up in one.

Example of a data breach notice with a detailed explanation of the situation (for more, head over here)How do you interpret a breach notice?

For that reason, you should never click through on any unsolicited breach notification email or message.

Change your logins (if relevant) and consider credit monitoring and a credit freeze.

3 weeks назад @ welivesecurity.com
MATCHBOIL: New tricks, same old evil intentions
MATCHBOIL: New tricks, same old evil intentions MATCHBOIL: New tricks, same old evil intentions

Later, in June 2026, ESET telemetry registered further MATCHBOIL samples, this time at a company in the energy sector.

MATCHBOIL then performs three HTTPS requests to the C&C server; each with a different purpose:The first request receives a numeric value from the C&C server.

2024 samplesThe earliest MATCHBOIL samples that we have seen have compilation timestamps from 2024.

]pro N/A 2025‑11‑10 MATCHBOIL C&C server hidden behind Cloudflare.

]com N/A 2025‑08‑12 MATCHBOIL C&C server hidden behind Cloudflare.

3 weeks, 4 days назад @ welivesecurity.com
Inside a brand deal scam targeting YouTube creators
Inside a brand deal scam targeting YouTube creators Inside a brand deal scam targeting YouTube creators

The platform also asks for the creator’s YouTube channel URL, which it uses to retrieve public information and generate a seemingly personalized experience.

How to stay safeIf you’re a social media influencer yourself, your Google account can be much more than “just” access to a YouTube channel.

Run Google’s Security Checkup, or open Security & sign-in in your Google account, and review recent security events and signed-in devices.

If you’re a YouTube creator yourself, you realize that your reputation ultimately defines your success.

A Google account can then sit at the center of your business: email, files, contacts, and the YouTube channel itself.

3 weeks, 5 days назад @ welivesecurity.com
The quest for simplicity: Why SMBs want advanced protection without the complexity
The quest for simplicity: Why SMBs want advanced protection without the complexity The quest for simplicity: Why SMBs want advanced protection without the complexity

The cybersecurity market is often making it tougher for SMBs to keep threats at bayCybersecurity has never been easy.

SMBs are very much in the crosshairs, as providers of critical infrastructure themselves or suppliers to firms operating in critical infrastructure.

Yet the identity of the adversary is arguably less important than the tactics they’re using to target global SMBs.

By offering teams AI assistance to improve productivity.

By offering teams AI assistance to improve productivity.

3 weeks, 6 days назад @ welivesecurity.com
This month in security with Tony Anscombe – September 2026 edition
This month in security with Tony Anscombe – September 2026 edition This month in security with Tony Anscombe – September 2026 edition

Autonomous AI agents go on a hacking spree, and Microsoft ships what used to be a year's worth of security patches in one go – here's how to keep paceAs another month draws to a close, ESET Chief Security Evangelist Tony Anscombe reviews some of the top cybersecurity stories that have made the news over the past 30 days while offering insights that they hold for your or your company's cyber-defenses.

Here's Tony's rundown of some of what stood out most in September 2026.

An OpenAI agent has broken into Australia's national healthcare database in what is the first known case of AI autonomously hacking a government network,Earlier in the month, Google announced that its models also escaped it…

1 month назад @ welivesecurity.com
Timeshare exit scams: From fake buyers to recovery fraud
Timeshare exit scams: From fake buyers to recovery fraud Timeshare exit scams: From fake buyers to recovery fraud

If an exit company cold calls you or makes 100% guaranteed promises of a swift exit, they’re likely to be a scammer.

If you’ve already paid a scam timeshare exit company, there’s still a chance you could get your money back if you act quickly.

What are the warning signs of a timeshare exit scam?

How can I check whether a timeshare exit company is legitimate?

What should I do if I've already paid a timeshare exit scam company?

1 month назад @ welivesecurity.com
Naked Security Naked Security
последний пост None
Help Net Security Help Net Security
последний пост 4 часа назад
CISA to federal agencies: Remediate exploited Ivanti Connect Secure vulnerabilities (CVE-2026-111357, CVE-2026-118527)
CISA to federal agencies: Remediate exploited Ivanti Connect Secure vulnerabilities (CVE-2026-111357, CVE-2026-118527) CISA to federal agencies: Remediate exploited Ivanti Connect Secure vulnerabilities (CVE-2026-111357, CVE-2026-118527)

CISA added two new Ivanti Connect Secure vulnerabilities (CVE-2026-111357, CVE-2026-118527) to its Known Exploited Vulnerabilities catalog on Friday, after Ivanti updated an earlier security advisory with details about the flaws.

According to Volexity researchers, who discovered the attack and reported it to Ivanti, the attackers were covertly turning the SSL VPN appliances into a foothold in the targeted organizations’ network.

All three flaws have been fixed by Ivanti, and customers using the Connect Secure SSL VPN appliance are advised to implement the provided updates.

“Volexity reports that the observed activity evades Ivanti’s Integrity Checker Tool, so a clean result does not rule ou…

4 часа назад @ helpnetsecurity.com
Google disrupts XCPE botnet, bans the company behind it
Google disrupts XCPE botnet, bans the company behind it Google disrupts XCPE botnet, bans the company behind it

Google shut down the servers behind XCPE, a backdoor hidden in the firmware of Android TV set-top boxes.

The 1.3 million figure covers the set-top boxes tied to this backdoor.

“While the overwhelming majority of the infected devices in the XCPE botnet are Android TV set-top boxes, we observed a number of other infected Android-based IoT devices, including telehealth devices, karaoke machines, and digital signage devices,” Google Threat Intelligence Group wrote.

It banned the company, plus any future subsidiaries and affiliates, from building certified Android devices or supplying software to certified vendors, and cut ties with the company.

Firmware integrity checks for certified Android TV…

4 часа назад @ helpnetsecurity.com
AI-powered infostealer picks out the most profitable parts of your stolen data
AI-powered infostealer picks out the most profitable parts of your stolen data AI-powered infostealer picks out the most profitable parts of your stolen data

A new Windows infostealer sends the data it steals to an AI model and asks it to rank the victim’s assets by how much money they could bring in, Cisco Talos has found.

The malware calls itself VOLTA-AUTODOXER and turned up through Talos’ CAIRN research effort, which tracks malware that uses AI.

The model’s job, Fetterman explained, is to stretch the stolen data and draw inferences that add to its value.

“After the collection and enrichment stages are complete, the data is assembled and structured locally in a file called ‘Identity_Report.txt’.

The question for defenders is not whether this pattern will appear elsewhere, but which phase it touches next,” Fetterman concluded.

5 часов назад @ helpnetsecurity.com
Second wave of refrigeration cyberattacks hits European supermarkets
Second wave of refrigeration cyberattacks hits European supermarkets Second wave of refrigeration cyberattacks hits European supermarkets

Three weeks after the attack that turned refrigeration units in French supermarkets into ovens overnight, similar cyberattacks have hit shops in other European countries and again caused refrigerated food to be spoiled.

Belgium, Luxembourg and Sweden affected“[In Belgium,] fridges and freezers have been affected at Delhaize, Carrefour and Spar, among others.

The attackers remotely switched the units’ evaporators to defrost mode, causing the fridges to warm up,” Belgian news agency Belga reported today.

The attack was made possible by remotely exploitable vulnerabilities in the monitoring systems’ internet-exposed management interfaces.

Subscribe to our breaking news e-mail alert to never mi…

5 часов назад @ helpnetsecurity.com
Trezor warns some of its wallets may hide a seed-stealing implant
Trezor warns some of its wallets may hide a seed-stealing implant Trezor warns some of its wallets may hide a seed-stealing implant

A Trezor Safe 5 sold by CryptoBilis, the reseller linked to the recent Ledger wallet drains, may contain a hidden implant that steals the owner’s recovery phrase, Trezor has warned.

It has made hardware wallets since 2014, and its current models are the Safe 3, Safe 5 and Safe 7.

A customer in Indonesia reported the implant to Trezor on October 28, through the company’s responsible disclosure program.

According to Trezor, the implant appears to work like the ones found in Ledger wallets, though the company won’t compare the two cases further and doesn’t know who is behind the attack.

CryptoBilis sold Trezor wallets in the region too.

7 часов назад @ helpnetsecurity.com
Chainalysis breached using “offensive agentic techniques”
Chainalysis breached using “offensive agentic techniques” Chainalysis breached using “offensive agentic techniques”

Blockchain analytics firm Chainalysis has suffered a cybersecurity incident that led to a data breach.

In October, the company detected external attackers using “offensive agentic techniques” to gain access to Chainalysis systems and internal tools.

However, the attackers managed to access some customer (user) IDs, full names, email addresses, and organization role labels for users provisioned on the company’s platform.

Chainalysis did not elaborate further on the offensive agentic techniques used by the attackers.

“Our investigators are observing never-seen-before laundering patterns with the stolen funds from the Binance exploit,” Chainalysis shared.

8 часов назад @ helpnetsecurity.com
FBI pins $6.3 billion Binance crypto heist on North Korea while scammers circle anxious users
FBI pins $6.3 billion Binance crypto heist on North Korea while scammers circle anxious users FBI pins $6.3 billion Binance crypto heist on North Korea while scammers circle anxious users

North Korea was behind the theft of more than $6 billion in cryptocurrency from Binance, the FBI has confirmed.

The FBI tied the attack to TraderTraitor, the North Korean group it named in the $1.5 billion Bybit hack of February 2025.

By early October 2025, blockchain analytics firm Elliptic had linked more than $2 billion in stolen crypto to North Korea for that year alone, most of it from the Bybit heist, along with more than thirty other hacks.

About $6.3 billion left Binance wallets on October 29, in what is likely the biggest crypto theft in history.

The company has replaced about 95% of the stolen assets with its own money, up from 90% in its previous update.

10 часов назад @ helpnetsecurity.com
DeepSeek open-sources Super-Agent, a coding agent that watches team chats for work
DeepSeek open-sources Super-Agent, a coding agent that watches team chats for work DeepSeek open-sources Super-Agent, a coding agent that watches team chats for work

Deepseek released a research prototype of dsh-superagent, a coding agent that does work on a GitHub repository for you.

Who can ask for workThe agent gets to work in two situations: an allowed user asks for something, or a rule your team wrote covers it.

You can also open up a chat or GitHub scope, and then anyone in it can request work just by mentioning the agent.

Explicit requests, such as an allowed user mentioning the agent, work in every mode.

By default the agent doesn’t turn on auto-merge under its own account, because GitHub credits the merge to whoever enabled it.

13 часов назад @ helpnetsecurity.com
The first ten lines of a command policy for AI coding agents
The first ten lines of a command policy for AI coding agents The first ten lines of a command policy for AI coding agents

In this Help Net Security interview, Vinay Thakker, CTO of KloudStax, explains how to set identity, credentials, and network limits for AI agents.

If you had to write the first ten lines of a command policy for a coding agent with terminal access, what would they say?

Anything that needs one goes through a broker the agent can’t read.

Network access is off except for the internal package mirror and the specific hosts this project needs.

Every command is logged with the agent’s identity and the task that triggered it, and a spend or runtime cap ends the session when it’s hit.

13 часов назад @ helpnetsecurity.com
Byoky: Open-source wallet for AI API keys
Byoky: Open-source wallet for AI API keys Byoky: Open-source wallet for AI API keys

Byoky is an open-source wallet for AI API keys, available as a Chrome and Firefox extension and as iOS and Android apps.

Apps that want those keys ask the wallet for access, and the wallet sends each request to the provider itself.

Byoky goes after the habit of pasting a key into a web app’s settings page to try a new tool.

Byoky copies the model of MetaMask, the crypto wallet that decentralized apps connect to: the app asks, the user approves, and one click revokes access.

The bridge rejects requests that lack a bridge token, a check meant to stop other programs on the same machine from spending the keys.

14 часов назад @ helpnetsecurity.com
Product showcase: Trust Onion uses rotating codewords to verify callers
Product showcase: Trust Onion uses rotating codewords to verify callers Product showcase: Trust Onion uses rotating codewords to verify callers

Trust Onion is a free app that gives trusted groups three rotating codewords to check who they are communicating with.

I tested the iPhone app with an older person, exploring setup and the tools available when a call or message raises concerns.

Get help from my group lets users select trusted contacts and send a callback request with an optional note.

Final thoughtsTrust Onion can help older people pause and check a request when a convincing call creates a sense of emergency.

Practicing with someone they trust can make that pause part of their response, even when they feel pressured to act.

14 часов назад @ helpnetsecurity.com
Ransomware gang talked AI agents into doing much of its dirty work
Ransomware gang talked AI agents into doing much of its dirty work Ransomware gang talked AI agents into doing much of its dirty work

The group behind the Aur0ra ransomware has been using AI agents to move through victim networks, collect credentials and work its way up to domain administrator access, according to Sophos.

In some networks, the agents gained domain management access, and three of those victims were later named on Aur0ra’s data leak site.

A red team cover storyTo get around the guardrails built into the AI tools, the attackers described the intrusions as authorized red team activity or diagnostic testing.

The researchers consider it highly likely that other ransomware groups will build AI agents into their operations too.

“AI can accelerate phases of the attack chain and reduce the level of technical aptitu…

15 часов назад @ helpnetsecurity.com
Week in review: Binance hit by $6.3 billion theft, impact of Brotli vulnerability
Week in review: Binance hit by $6.3 billion theft, impact of Brotli vulnerability Week in review: Binance hit by $6.3 billion theft, impact of Brotli vulnerability

Several AI security market categories are headed for bigger platformsIn this interview with Help Net Security, Jonathan Care, Lead Analyst and Practice Lead AI at KuppingerCole Analysts, compares AI security startups to the early fraud market he helped define at Gartner.

Qualys CISO on what security teams can do as exploit campaigns growIn this Help Net Security interview, Nathan Smolenski, CISO at Qualys, talks about how security teams can handle the growing volume of AI-discovered vulnerabilities.

Security teams often spend too much time moving between tools to piece together an incident.

Integrated Security Operations Center (ISOC) solutions aim to reduce that work by bringing detection,…

1 day, 11 hours назад @ helpnetsecurity.com
Assad regime hacker who caused $136 billion market drop sentenced to 42 months
Assad regime hacker who caused $136 billion market drop sentenced to 42 months Assad regime hacker who caused $136 billion market drop sentenced to 42 months

A Syrian man who used a hijacked news agency Twitter account to post a fake report of explosions at the White House has been sentenced to 42 months in prison, the US Department of Justice has announced.

The scheme ran from as early as August 2011 until January 2024, and Agha spent more than a decade on the run.

Punishing the pressTo spread the regime’s propaganda, Agha hacked approximately 47 Western media outlets, businesses, NGOs, and US and allied government entities.

The post caused a temporary $136 billion drop in the value of the stocks that make up the Dow Jones Industrial Average.

On two occasions, he tried to take over the White House’s social media page by stealing usernames and p…

3 days, 7 hours назад @ helpnetsecurity.com
Shufti ties AI agent actions to verified owners and permissions
Shufti ties AI agent actions to verified owners and permissions Shufti ties AI agent actions to verified owners and permissions

Shufti launches Know Your Agent (KYA), an AI agent verification solution designed to verify autonomous AI agents acting on behalf of individuals and businesses.

Shufti KYA helps businesses accept authorized AI agents while blocking unauthorized or high-risk activity that could lead to AI agent fraud or chargeback disputes.

AI agent authorization starts with a principal that sets a mandate for each AI agent, covering permitted actions, limits, expiry, and revocation.

“Shufti Know Your Agent verifies every AI agent request with a verified owner, a clear mandate, and a record that holds up under review.

This allows businesses to adopt AI agent automation with full human approval over agent per…

3 days, 7 hours назад @ helpnetsecurity.com
IT Security Guru IT Security Guru
последний пост None
SecurityTrails
последний пост None
Блоги 👨‍💻
Бизнес без опасности Бизнес без опасности
последний пост None
Жизнь 80 на 20 Жизнь 80 на 20
последний пост None
ZLONOV ZLONOV
последний пост None
Блог Артема Агеева Блог Артема Агеева
последний пост None
Киберпиздец Киберпиздец
последний пост None
Schneier on Security Schneier on Security
последний пост 8 часов назад
AI Vulnerability Finding
AI Vulnerability Finding AI Vulnerability Finding

A comment:

3% of ‘critical’ software security bugs, in all of recorded history, have been found in the last month. This is on pace to find another ~100,000 bugs this year alone, adding ~26% more vulnerabilities to the all time total Do you realize how fucking insane that is?

Yes. It is a new world out there.

8 часов назад @ schneier.com
Friday Squid Blogging: Bigfin Squid Off California Coast
Friday Squid Blogging: Bigfin Squid Off California Coast Friday Squid Blogging: Bigfin Squid Off California Coast

Neat video:

The sighting, announced September 2, marks the first time anyone has spotted a live bigfin squid, which belongs to the Magnapinna genus, in the northeastern Pacific Ocean.

As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.

Blog moderation policy.

2 days, 23 hours назад @ schneier.com
Bloatware in Aftermarket Auto Parts
Bloatware in Aftermarket Auto Parts Bloatware in Aftermarket Auto Parts

This story is interesting:

One Civic owner purchased a cheap aftermarket head unit off Amazon, and decided to have Claude work its magic on it, like it would a smart TV. What was reportedly discovered isn’t surprising, but is worth knowing about.

Among the pre-installed bloatware—­or spyware, if you’re being less charitable­—was a voice assistant equipped with WebView, an Android system component that lets apps display content off the web. This apparently always used about a third of processing power, even while idle, which isn’t great. There were also Baidu location services, a call recorder (!), a DAB radio client that is pretty much useless in the U.S., and Adobe Acrobat, presumably so y…

3 days, 4 hours назад @ schneier.com
Studying Fraudulent North Korean IT Workers
Studying Fraudulent North Korean IT Workers Studying Fraudulent North Korean IT Workers

Researchers set up a fake start-up company to study fraudulent North Korean IT workers.

5 days, 9 hours назад @ schneier.com
Hiding Capabilities in AI Models
Hiding Capabilities in AI Models Hiding Capabilities in AI Models

Interesting research: “AI Models Can Provably Hide Arbitrary Capabilities”

Abstract: Capability evaluations aim to surface dangerous model behaviors before deployment, but their reliability depends on the assumption that hidden capabilities can be elicited. We show this assumption does not hold under adversarial conditions by constructing backdoor attacks that embed encrypted neural networks within host model weights, decrypting and executing them only upon receiving a secret trigger. Using digital lockers, these hidden circuits remain provably hard to elicit and interpret under cryptographic assumptions, even given full access to model weights, extending prior work from hiding fixed string…

6 days, 9 hours назад @ schneier.com
Bias in Qwen3-Coder Model
Bias in Qwen3-Coder Model Bias in Qwen3-Coder Model

Interesting research:

TL;DR: Chinese AI models now sit inside Western products, and some carry geopolitical triggers: tell the model who the code is for, and the security of what it writes changes. For the first time, we showed that this vulnerability lives in the model’s weights, and that removing the model’s CCP alignment removes it. One word tilts the code against Americans. Ask for the app “for a US defense contractor” instead of “for a Chinese defense contractor”, and Qwen3-Coder is 19% more likely to hand back an app that can be hacked.

...

1 week назад @ schneier.com
Friday Squid Blogging: Increasing Squid Populations
Friday Squid Blogging: Increasing Squid Populations Friday Squid Blogging: Increasing Squid Populations

This article in Nature argues that it’s due to an overfishing of predators and warming sea temperatures.

As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.

Blog moderation policy.

1 week, 2 days назад @ schneier.com
Compromised TLS Certificates
Compromised TLS Certificates Compromised TLS Certificates

The Indian CA eMudhra Limited has eight TLS certificates with laughably weak private keys:

The compromised eMudhra keys were defective at a level that’s challenging the imagination of many of the engineers studying the incident. A normal size for a NIST P-384 elliptic curve cryptography private key contains roughly 384 bits of entropy, a size allowing almost 2384, or a number with 116 digits, different possibilities. The private key sizes of the compromised keys ranged from 3 to 8 bits. Astonishingly, the private keys were 4, 56, 66, 115, 155, 156, 230, 237...

1 week, 3 days назад @ schneier.com
New Serious PHP Vulnerabilities Released and Patched
New Serious PHP Vulnerabilities Released and Patched New Serious PHP Vulnerabilities Released and Patched

PHP maintainers have released two critical vulnerabilities:

PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix two critical vulnerabilities that can allow unauthenticated remote code execution. All PHP users are strongly encouraged to update immediately. Who is at risk: all PHP installations serving web requests, including PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed. We consider the risk highest for mod_php, with a demonstrated exploit where an unauthenticated request can trigger the attack before any application code runs.

The vulnerabilities:...

1 week, 4 days назад @ schneier.com
Workshop on Economics and Information Security (WEIS) Archive
Workshop on Economics and Information Security (WEIS) Archive Workshop on Economics and Information Security (WEIS) Archive

There’s a new archive of all the papers from twenty-five years of the Workshop on Economics and Information Security (WEIS).

Really nice resource. It’s fun to reread my 2002 essay on the economics of information security.

1 week, 5 days назад @ schneier.com
Possible new Cellebrite iPhone Radio Zero-Day
Possible new Cellebrite iPhone Radio Zero-Day Possible new Cellebrite iPhone Radio Zero-Day

Justin.sh is reporting on a confidential Cellebrite document that has been leaked to him:

Cellebrite calls it Advanced Unlocks (AU from here on), not to be confused with the “advanced unlocking services” they’ve marketed for years. A press release from earlier this year confirms AU is a new product for 2026.

[…]

According to Cellebrite, AU: is a “next-generation AFU vector that is more resilient to Apple’s OS changes”

works with Stolen Device Protection enabled, which tightens USB restrictions

is enabled by a dedicated appliance with a stated range (!) of about 8 meters...

1 week, 6 days назад @ schneier.com
Training AIs to Solve CAPTCHAs
Training AIs to Solve CAPTCHAs Training AIs to Solve CAPTCHAs

Interesting research:

Abstract: Vision-language models (VLMs) can solve visual CAPTCHAs without task-specific training, but the agents built on them approach every challenge from scratch. For such an agent, the hundredth instance of a familiar puzzle costs as much time and compute as the first. Specialized detectors invert the trade-off, answering in milliseconds but only for categories they were trained on. Neither improves with exposure. We study what changes when a solver improves with use. Our system pairs a fine-tuned YOLOv8 detector with an open-weight VLM behind a confidence-based router, and runs entirely from screenshots and operating-system input events, with no browser automation…

2 weeks назад @ schneier.com
Friday Squid Blogging: Squid Before the Chicxulub Meteor Impact
Friday Squid Blogging: Squid Before the Chicxulub Meteor Impact Friday Squid Blogging: Squid Before the Chicxulub Meteor Impact

New research shows that squid lived all around the globe even before the Cretaceous-Paleogene mass extinction event.

As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered.

Blog moderation policy.

2 weeks, 2 days назад @ schneier.com
Backdooring Open-Weight AI Models
Backdooring Open-Weight AI Models Backdooring Open-Weight AI Models

This is a problem:

Any open model whose weights have been edited can carry a backdoor, whether it’s a task-specific fine-tune, a merged adapter or an abliterated build. We have abliterated models in the title because it’s the most popular reason people download modified weights without verifying what’s inside. Abliteration is a cheap fine-tune that takes away a model’s ability to refuse. You find the direction in the weights that carries “no” and subtract it. The model then answers things a safety-tuned version would turn down. It began as a research trick and it’s now routine before people upload a model to Hugging Face, where you’ll find abliterated builds of most of the popular open weig…

2 weeks, 3 days назад @ schneier.com
Measuring Human Cryptanalysis Effort
Measuring Human Cryptanalysis Effort Measuring Human Cryptanalysis Effort

Matthew Green has a new site that tries to estimate the number of cryptanalyst-hours that have been spent analyzing different public-key algorithms:

Abstract: We estimate how much public cryptanalysis each public-key assumption has received, using the literature itself as the instrument. From roughly sixteen thousand candidate papers we classify cryptanalytic work on ECDLP, structured and plain lattices, syndrome decoding and their comparators, then convert papers into estimated research-allocation years through a person-level author map. These publication-based estimates may substantially overstate actual time spent. Lattices have overtaken elliptic curves in this cumulative measure only r…

2 weeks, 4 days назад @ schneier.com
Krebs On Security
последний пост 1 week, 5 days назад
Widespread PHP Flaw May Cause Many Site Outages Today
Widespread PHP Flaw May Cause Many Site Outages Today Widespread PHP Flaw May Cause Many Site Outages Today

Earlier today, PHP released an emergency security update to fix two critical bugs that can allow an attacker to execute code of their choosing on a vulnerable server.

Reuters reports that government websites in Europe and elsewhere went offline today after the PHP vulnerabilities were disclosed.

Wiz said that prior to the PHP bugs being publicly disclosed, the company worked with the PHP team, Calif and OpenAI to measure the size of the problem and coordinate patch verification and disclosure.

The PHP zero-day vulnerabilities are being tracked by their CVE numbers, CVE-2026-109618 and CVE-2026-109619, and they affect all web servers running PHP 5.4 or later.

“A vulnerability in core PHP rea…

1 week, 5 days назад @ krebsonsecurity.com
Feds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site
Feds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site Feds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site

According to the FBI, ShinyHunters has extorted more than $70 million from victims so far this year.

He also said Mr. Dubrovsky has misrepresented himself as a Cypfer founder, and is not a shareholder.

In 2020, Aon aquired Cytelligence, a security consulting firm where Mr. Tobok was founder and CEO and Mr. Dubrovsky was a managing partner.

Experts say ransomware victims are typically directed by their insurance provider to work with a specific incident response firm.

But that ransom payment did not stop future extortion attempts using the same stolen data.

2 weeks назад @ krebsonsecurity.com
U.K. Sanctions Cryptomus for RU Money Laundering
U.K. Sanctions Cryptomus for RU Money Laundering U.K. Sanctions Cryptomus for RU Money Laundering

The sanctions freeze any Cryptomus assets at U.K. banks, and bar British companies from offering it any business, virtual or otherwise.

The blockchain data-crunching firm Chainalysis said the U.K. sanctions target the broader infrastructure supporting Russia’s wartime economy.

“Cryptomus and Heleket have emerged as major payment hubs for illicit activity,” Chainalysis wrote in an October 8 blog post.

Sanders said the U.K. sanctions on Cryptomus are important because Canada’s sanctions against the platform were ultimately unenforceable and uncollectible.

“A fine doesn’t stop a cryptocurrency payment processor from processing payments,” Sanders wrote on LinkedIn.

2 weeks, 5 days назад @ krebsonsecurity.com
Microsoft Patches More Than 1,400 Security Flaws
Microsoft Patches More Than 1,400 Security Flaws Microsoft Patches More Than 1,400 Security Flaws

Microsoft today issued updates to fix more than 1,400 security vulnerabilities in its Windows operating systems and other software.

CVE-2026-96951 is a security feature bypass in the Windows Shell that affects Windows 10 and 11 systems, as well as some Server versions.

Windows 10 users might be wondering if they can still expect security updates after this month.

Microsoft had been slated to stop shipping updates for Windows 10 systems in October 2025, but ended up adding another year of free updates after considerable pushback.

Satnam Narang at Tenable said the number of flaws fixed this month far surpasses the previous record-setting year 2020, when Microsoft patched 1,261 CVEs.

2 weeks, 5 days назад @ krebsonsecurity.com
FBI Arrests Founder of Ransomware Negotiation Firm
FBI Arrests Founder of Ransomware Negotiation Firm FBI Arrests Founder of Ransomware Negotiation Firm

The New York Times reported today that the FBI has arrested a Canadian man in Pennsylvania on suspicion of assisting ShinyHunters.

The Times story did not identify the man, nor did a statement on Twitter/X about the arrest from FBI Director Kash Patel.

Another shared that control over the ShinyHunters investigation has been centralized at an FBI field office in Texas.

According to LinkedIn, Cypher was co-founded by a Canadian man named Edward Dubrovsky, who is now associated with another Canadian security firm called CyberSteward.

According to the FBI, the group has extorted more than $70 million from victims so far this year.

3 weeks, 2 days назад @ krebsonsecurity.com
ShinyHunters Extorted Boeing Spin-off Prior to Arrests
ShinyHunters Extorted Boeing Spin-off Prior to Arrests ShinyHunters Extorted Boeing Spin-off Prior to Arrests

The Dutch daily RTL reported on Sept. 29 that investigators suspect Van der Stap tried to orchestrate at least two murders.

According to RTL, the murders were allegedly to be committed abroad, and there are indications Van der Stap gave the order for these attacks.

In an interview with KrebsOnSecurity on September 9, Van der Stap described his new role as “offensive security lead” at the Dutch cybersecurity company Neo Security, saying the job involved probing client networks for security vulnerabilities.

Korper said Dutch forensic investigators visited his office on September 15, the night Van der ⁠Stap was arrested in a dramatic police raid that reportedly involved flash bang grenades.

“Y…

3 weeks, 5 days назад @ krebsonsecurity.com
Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation
Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation

Authorities in the Netherlands have arrested a 23-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions by the prolific hacker group ShinyHunters.

Van der Stap is currently employed as offensive security lead at the Dutch company Neo Security, which did not respond to requests for comment.

But not long after that interview, the Dutch hacker abruptly stopped replying to messages.

One source said a colleague of theirs personally witnessed Dutch authorities carting items out of Van der Stap’s residence.

Speaking with reporters from Bloomberg in 2024, Van der Stap said that singular focus in turn fueled his desire to carry out cyberattacks.

1 month назад @ krebsonsecurity.com
U.S. Soldier Gets 70 Months in Prison for AT&T, Verizon Extortions
U.S. Soldier Gets 70 Months in Prison for AT&T, Verizon Extortions U.S. Soldier Gets 70 Months in Prison for AT&T, Verizon Extortions

A U.S. Army soldier who pleaded guilty to hacking into multiple telecommunications companies and stealing mobile call and text metadata for more than 100 million AT&T customers in 2024 was sentenced to 70 months in federal prison today and ordered to pay nearly $300,000 in restitution to victims.

Kiberphant0m claimed to have hacked into more than dozen telecommunications companies worldwide, including Verizon’s Push-to-Talk business, and publicly extorted these companies in exchange for a promise not to publish the stolen data.

Less than a month later, Wagenius was arrested and charged in two separate federal indictments, and soon pleaded guilty to all counts in both cases.

In 2019, Schuchm…

1 month, 1 week назад @ krebsonsecurity.com
Data Broker Radaris Loses Domains in Privacy Fight
Data Broker Radaris Loses Domains in Privacy Fight Data Broker Radaris Loses Domains in Privacy Fight

In February 2024, Radaris was sued by Atlas Data Privacy Corp, a company that has been pursuing data brokers alleged to be violating a New Jersey statute called Daniel’s Law.

KrebsOnSecurity doubled down and showed how the Lubarsky brothers built and operated Radaris and other data broker companies using a fictitious CEO’s name.

All told, the New Jersey court has so far transferred 14 domain names from the Radaris family of companies to Atlas.

Sherman said federal lawmakers have long faced intense lobbying by the technology industry against more restrictive U.S. data privacy laws, but that many powerful industries are now working against passing comprehensive data privacy legislation.

The l…

1 month, 2 weeks назад @ krebsonsecurity.com
Microsoft Plugs Nearly 1,000 Security Holes
Microsoft Plugs Nearly 1,000 Security Holes Microsoft Plugs Nearly 1,000 Security Holes

Microsoft Corp. today issued updates to plug at least 974 security holes in its Windows operating systems and other software, by far its biggest single patch batch ever.

This month’s patch bundle obliterates the software giant’s previous record set in July, when it released updates for at least 570 security vulnerabilities.

Among the more serious critical flaws this month is CVE-2026-69730, a DNS weakness present in Windows Server 2012 onward and on Windows 10.

And at the rate these Windows patch releases are ballooning in size, it’s probably best not to let them pile up month after month.

Enterprise Windows admins will want to keep an eye on askwoody.com for news of any updates that appear…

1 month, 3 weeks назад @ krebsonsecurity.com
FBI Probes Service Selling 153M+ Drivers Licenses
FBI Probes Service Selling 153M+ Drivers Licenses FBI Probes Service Selling 153M+ Drivers Licenses

A new identity theft service launched on the dark web this week is selling digital scans of more than 153 million drivers licenses from people in the United States and Canada.

Curiously, the identity records include not only drivers licenses but also marijuana dispensary cards.

Some of the records list their “source” as “CDL,” presumably short for “commercial drivers license.

Also, only some of those who helped with this research said they showed their drivers license at the airport on the day of their travel.

Baldwin said the Nexus identity theft service presents multiple serious security and privacy threats, noting that state-issued drivers licenses are commonly used as proof of one’s ide…

2 months назад @ krebsonsecurity.com
Two Alleged ‘TeamPCP’ Hackers Arrested in Australia
Two Alleged ‘TeamPCP’ Hackers Arrested in Australia Two Alleged ‘TeamPCP’ Hackers Arrested in Australia

The malware allows TeamPCP’s hackers to steal credentials that let them publish malicious versions of those software development tools, too.

“TeamPCP has stated the competition is a recruiting opportunity and they intend to purchase all meaningful access harvested from participants’ campaigns,” the security firm Dataminr wrote.

Deadcatx3, a nickname that has been flagged by multiple security firms as an alias used by TeamPCP.

Charlie Eriksen is a security researcher at Aikido Security who has closely followed TeamPCP’s cybercrime campaigns.

“They managed to wake up Microsoft to the fact that they had become negligent in terms of security,” Eriksen said.

2 months, 1 week назад @ krebsonsecurity.com
Who’s Tracking You? Use This New Service to Find Out
Who’s Tracking You? Use This New Service to Find Out Who’s Tracking You? Use This New Service to Find Out

It can be daunting to determine who’s responsible for showing ads on the websites we visit, or who’s harvesting data from the mobile apps we use every day.

Not anymore: A powerful and free new service called DecryptAds scrapes and correlates this adtech data and makes it simple to quickly learn a great deal about the entities that are tracking you.

“It’s an adtech tool but we’re trying to approach adtech from a security perspective,” Edwards said.

DecryptAds reports that Between Digital is collecting ad data on approximately 55,000 partner websites.

Bear in mind that ad blockers often do little to block ads and/or tracking that occurs from within mobile apps that users have chosen to instal…

2 months, 2 weeks назад @ krebsonsecurity.com
Microsoft Plugs Nearly 400 Security Holes
Microsoft Plugs Nearly 400 Security Holes Microsoft Plugs Nearly 400 Security Holes

Microsoft today released updates to remedy at least 398 security vulnerabilities in its Windows operating systems and supported software, including one weakness that is already being actively exploited and two others that were publicly detailed prior to today.

August’s overstuffed bundle of patch joy from Microsoft did not eclipse its recording breaking release of more than 570 security updates last month, but it is double June’s then-record batch of nearly 200 fixes.

The other publicly disclosed flaw is CVE-2026-72971, a low-impact local tampering vulnerability that Microsoft reckons is unlikely to be exploited.

By all accounts, AI is quite good at finding security holes in software.

“Don’…

2 months, 3 weeks назад @ krebsonsecurity.com
Canadian Man Pleads Guilty in Snowflake Extortions
Canadian Man Pleads Guilty in Snowflake Extortions Canadian Man Pleads Guilty in Snowflake Extortions

Snowflake responded to the data thefts by increasing password complexity requirements and enforcing multi-factor authentication.

A little more than a month later, Canadian authorities arrested Moucka on a provisional warrant from the United States.

“Moucka used the stolen data of a government officer and members of a then-former government officer’s immediate family in this re-extortion attempt,” reads a statement from the Justice Department.

Moucka pleaded guilty to four criminal counts, including computer fraud, wire fraud, aggravated identity theft, and conspiracy.

Ultimately, it will be up the federal judge how much time Moucka actually serves for his extensive cybercriminal rap sheet.

2 months, 4 weeks назад @ krebsonsecurity.com
Graham Cluley Graham Cluley
последний пост 3 days, 9 hours назад
Hackers leak personnel data of 41,000+ Homeland Security staff, including ICE and border agents
Hackers leak personnel data of 41,000+ Homeland Security staff, including ICE and border agents Hackers leak personnel data of 41,000+ Homeland Security staff, including ICE and border agents

More than 41,000 people working for the US Department of Homeland Security, including ICE agents, have had their details published online by a group of hacktivists.

As TechCrunch reports, the leaked records include the names, job titles, work email addresses, phone numbers, abd office locations.

More than half of the leaked records relate to US Customs and Border Protection (CBP) employees, typically found at airports, seaports, and land border crossings.

Around 10,000 ICE employees have had their records breached, and almost 1,000 members of the Cybersecurity and Infrastructure Security Agency (CISA).

The leaked data has been published online, under the title "Icepick", and can be either d…
3 days, 9 hours назад @ bitdefender.com
BYOD cyberattack diverts ambulances and cancels classes at University of New Mexico health center

Ambulances were diverted, surgeries cancelled, and medical students sent home from classes after a ransomware group attacked the University of New Mexico's Health Sciences Center (HSC) this week. Read more in my article on the Fortra blog.

4 days, 3 hours назад @ fortra.com
Smashing Security podcast #490: How Jared Kushner’s iPhone was allegedly hacked twice
Smashing Security podcast #490: How Jared Kushner’s iPhone was allegedly hacked twice Smashing Security podcast #490: How Jared Kushner’s iPhone was allegedly hacked twice

You are suffering a little bit, not that our listeners will be able to tell, but if anyone sees you on video.

Well, everything's a little bit political, but this is fundamentally a cybersecurity podcast.

And it won't necessarily come back and say, "I don't think you should be doing this," or, "Have you sought some help?"

Maybe we should turn a little bit to what organisations can actually do about it.

I'm going to do it the following Thursday, or I'm going to do it some other time, or I'm going to create an account that doesn't go back to me, but I can still support my favourite places.

4 days, 20 hours назад @ grahamcluley.com
Hive ransomware affiliate jailed, years after FBI infiltrated the gang’s systems
Hive ransomware affiliate jailed, years after FBI infiltrated the gang’s systems Hive ransomware affiliate jailed, years after FBI infiltrated the gang’s systems
A Ukrainian man has been sentenced to 70 months in a US prison for his role in a series of ransomware attacks.

He was also an early affiliate of the Hive ransomware-as-a-service (RaaS) operation which targeted businesses and, in particular, organisations working in healthcare.

The FBI later warned that Hive had extorted US $100 million from businesses and organisations globally in a period of just 18 months.

The DOJ said that the operation saved corporate victims of Hive over US $130 million in ransom payments.

At the time I speculated that the take-down of Hive may lead to the identification and possible apprehension of some of those involved in Hive ransomware attacks.

5 days, 4 hours назад @ bitdefender.com
Hacker leaks 281 GB of data from Germany’s far-right AfD party
Hacker leaks 281 GB of data from Germany’s far-right AfD party Hacker leaks 281 GB of data from Germany’s far-right AfD party

Germany's far-right AfD (Alternative für Deutschland) party has confirmed that it has suffered a security breach, after a hacker published what appear to be hundreds of thousands of the controversial political party's internal emails.

Earlier this week, the AfD admitted that its hosting provider had been hacked in September, and that some of its mailboxes had been copied.

What is unusual is that the leaked emails are not published on the site directly.

Indeed, party sources told the media that although the leaked emails appeared to be authentic, the AI-generated summaries appeared to contain several inaccuracies.

The full corpus of 281 GB of stolen messages and files has been made available…

1 week, 3 days назад @ bitdefender.com
Smashing Security podcast #489: How a brand new crypto wallet came with a spy inside
Smashing Security podcast #489: How a brand new crypto wallet came with a spy inside Smashing Security podcast #489: How a brand new crypto wallet came with a spy inside

Smashing Security, episode 489, How a Brand New Crypto Wallet Came with a Spy Inside, with Graham Cluley and special guest Lianne Potter.

So a bit of a War of the Roses thing going on there with that reference to Burnham.

What I'm going to do is I'm going to describe things, and the more dangerous the thing is, the faster it will click.

But I'm going to say it's probably dodgy, but oh, the curiosity would get the better of me.

But I'm actually in the same boat as most people because this film has been censored for nearly half a century.

1 week, 4 days назад @ grahamcluley.com
Police arrest Qilin ransomware suspect on holiday, as links made to Synnovis hack that contributed to patient’s death
Police arrest Qilin ransomware suspect on holiday, as links made to Synnovis hack that contributed to patient’s death Police arrest Qilin ransomware suspect on holiday, as links made to Synnovis hack that contributed to patient’s death

A 28-year-old Russian man has been arrested by German police, suspected of being a key member of the Qilin ransomware gang.

As BBC News reports, detectives have linked the man to the 2024 attack against blood-testing firm Synnovis, that disrupted London hospitals, and resulted in the death of a patient.

The suspect, who has been named by German media only as "Vladimir K" was originally detained in May in Japan, after he travelled there on holiday.

The incident is said to have crippled Synnovis’s IT systems, and caused a critical shortage of O-type blood in hospitals.

No ransom was paid by Synnovis, a decision the firm made jointly with the NHS trusts to which it provides services.

1 week, 6 days назад @ bitdefender.com
Irish police force has its Twitter hacked in cryptocurrency scam
Irish police force has its Twitter hacked in cryptocurrency scam Irish police force has its Twitter hacked in cryptocurrency scam

The official @GardaInfo and @GardaTraffic Twitter accounts of Garda Síochána were accessed by an unauthorised third party who posted cryptocurrency-related messages on Wednesday evening, potentially reaching hundreds of thousands of users.

The messages claimed that followers were eligible to claim free cryptocurrency through an airdrop.

The problem, however, is not just that a hacker found themselves with the ability to post fraudulent messages posing as the Irish police.

The Garda is not the only police force to have ever suffered a security breach on its Twitter account.

In 2022, the official Twitter account of the Philadelphia Police Department was compromised and used to post what appea…

2 weeks, 3 days назад @ bitdefender.com
Krybit ransomware: what you need to know

Krybit is a fast-growing ransomware gang that was hacked by a rival, hit back, and is still extorting victims. Find out how it works, who it has targeted, and what organisations can do to protect themselves. Read more in my article on the Fortra blog.

2 weeks, 3 days назад @ fortra.com
Smashing Security podcast #488: How a ransomware negotiator ended up arrested at his own conference
Smashing Security podcast #488: How a ransomware negotiator ended up arrested at his own conference Smashing Security podcast #488: How a ransomware negotiator ended up arrested at his own conference

How a ransomware negotiator ended up arrested at his own conference, with Graham Cluley and special guest Paul Ducklin.

I don't know if you know that.

And then I became a freelancer and then I thought, oh boy, I'm going to open the doors to everybody.

And he is the Canadian co-founder of a ransomware negotiator firm called— I don't know how to pronounce this.

There's no breach so unimportant that you can just say, don't worry folks, carry on, nothing to see here.

2 weeks, 4 days назад @ grahamcluley.com
GTA 6 leaker threatens to release full playable version of game ahead of official launch
GTA 6 leaker threatens to release full playable version of game ahead of official launch GTA 6 leaker threatens to release full playable version of game ahead of official launch

The hacker behind a high-profile string of leaks involving the upcoming release of the Grand Theft Auto (GTA) 6 videogame has threatened to release a complete, playable build.

CyberLeek says that if the GTA 6 game is released on physical disk, and a public apology is made, it will step back from its threats.

As ever, videogame fans should be very wary of believing anybody who offers a download of a supposedly leaked game.

Besides which, the real, genuine GTA 6 is due to be released on video game platforms on 19 November.

It is not worth infecting your computer, or losing money on a dodgy crypto coin, just to see it a few weeks early.

2 weeks, 6 days назад @ bitdefender.com
$10 million bounty offered for Chinese Hafnium hacker accused of Microsoft Exchange Server mega-attack
$10 million bounty offered for Chinese Hafnium hacker accused of Microsoft Exchange Server mega-attack $10 million bounty offered for Chinese Hafnium hacker accused of Microsoft Exchange Server mega-attack

Zhang is charged alongside 34-year-old Xu Zewei with malicious cyber activity against US computer systems between February 2020 and June 2021.

The following the year the pair allegedly exploited vulnerabilities in Microsoft Exchange Server to steal further information.

Furthermore, if findings by security firm SentinelOne are to be believed, Zhang's Shanghai Firetech filed multiple software patents about extract data from computers.

Xu, for instance, was arrested at Milan airport in July 2025 and extradited to the United States in April this year.

China's Foreign Ministry opposed Xu's extradition, accusing the United States of fabricating charges against him.

3 weeks, 3 days назад @ bitdefender.com
Smashing Security podcast #487: Clippy’s crypto comeback
Smashing Security podcast #487: Clippy’s crypto comeback Smashing Security podcast #487: Clippy’s crypto comeback

But do you actually know whether both of them can do the job?

Now, I don't know how good a swimmer you are, Danny.

I don't know about you, but I'm having 3 or 4 calls a day from an unknown number.

And I would imagine a company like Hack The Box has got great visibility as to what is actually going on out there.

And so I think that's the unique part here is it truly does have a pressure-tested element to it.

3 weeks, 4 days назад @ grahamcluley.com
N0n ransomware: what you need to know

N0n is a newly-emerged cyber extortion gang. The group was first spotted in the middle of September 2026, and within days it had published on its dark web leak site details of what it claimed to be around a dozen victims. Since then, the tally has continued to grow. Read more in my article on the Fortra blog.

1 month назад @ fortra.com
FBI tells ShinyHunters members to turn themselves in, after arrest of alleged leader
FBI tells ShinyHunters members to turn themselves in, after arrest of alleged leader FBI tells ShinyHunters members to turn themselves in, after arrest of alleged leader

The FBI has a very simple message for the ShinyHunters gang: give yourselves up.

The FBI describes the man arrested in Amsterdam as "one of the alleged leaders of ShinyHunters", although Dutch police say only that he played a role.

The warning to remaining members of ShinyHunters follows particularly embarrassing episode for the FBI, which recently confirmed it had had its job application portal compromised by the gang.

According to ShinyHunters, it gained access to the FBI's data by exploiting a recently-patched flaw (CVE-2026-35273) in Oracle PeopleSoft PeopleTools.

The truth is that the arrest came a week or so before the compromise of the FBI became headline news.

1 month назад @ bitdefender.com
Компании 🏢
Блог Касперского Блог Касперского
последний пост 7 часов назад
Как удаленно отключить камеру видеонаблюдения: проблема и решение | Блог Касперского

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: 0d697b7db0e95a6580b88e9a4b8e961fServer IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-11-02T16:00:13+03:00Config id: 339Faithfully yours, nginx.

7 часов назад @ kaspersky.ru
Как скачивать и читать электронные книги безопасно | Блог Касперского
Как скачивать и читать электронные книги безопасно | Блог Касперского Как скачивать и читать электронные книги безопасно | Блог Касперского

Вопреки распространенному заблуждению, в эпоху цифры люди не перестали любить книги — просто их уже давно читают не только на бумаге.

Год назад мы также рассказывали про вредоносные «книги» на турецком и арабском языках.

Зачастую эти поддельные сайты полностью функциональны: на них точно так же можно искать и скачивать книги, и дизайн практически неотличим от оригинала.

Одна из самых простых рекомендаций — пользоваться официальными книжными магазинами, и не только по соображениям авторских прав.

Таким образом вы защитите свои данные и деньги и сможете спокойно скачивать и читать вашу любимую литературу.

3 days, 6 hours назад @ kaspersky.ru
Риски из-за слабых ключей в сертификатах УЦ eMudhra и необходимые меры по реагированию | Блог Касперского

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: c37d2c17b96ad93f72f21acf52f07186Server IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-10-29T16:00:22+03:00Config id: 339Faithfully yours, nginx.

4 days, 7 hours назад @ kaspersky.ru
Применяем подход Secure by Design и кибериммунитет в защите ИИ-систем

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: 4e5cae3ff5837cf370c8bf305d03c2b0Server IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-10-30T14:00:34+03:00Config id: 339Faithfully yours, nginx.

4 days, 9 hours назад @ kaspersky.ru
Одиссея, информационная безопасность и торренты | Блог Касперского

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: d6b768fbc443335b282efe8a58868231Server IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-10-26T15:00:14+03:00Config id: 339Faithfully yours, nginx.

1 week назад @ kaspersky.ru
Технология, блокирующая DGA-домены | Блог Касперского

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: 6e1eb2ff9ba52d21e2eb9108c143beafServer IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-10-23T17:00:39+03:00Config id: 339Faithfully yours, nginx.

1 week, 3 days назад @ kaspersky.ru
Чем опасны уязвимости PHP для простых пользователей и их устройств | Блог Касперского

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: 704ec22d9a79fd07b89340a5c2d02b67Server IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-10-22T23:00:36+03:00Config id: 339Faithfully yours, nginx.

1 week, 4 days назад @ kaspersky.ru
PHP2Shell: как защитить сервер | Блог Касперского

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: 0bd9145f797a3fff09593e8e6fc88bd4Server IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-10-21T20:00:35+03:00Config id: 335Faithfully yours, nginx.

1 week, 5 days назад @ kaspersky.ru
ИИ-инструменты для доксинга: как изменились технологии онлайн-слежки | Блог Касперского

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: a48e6a868074b4c2b77295af18788714Server IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-10-20T17:00:12+03:00Config id: 335Faithfully yours, nginx.

1 week, 6 days назад @ kaspersky.ru
Как составить резюме с ИИ: советы и готовый промпт | Блог Касперского

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: 65c81bea022dea0314bb3ec1fb8b3228Server IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-10-15T14:00:29+03:00Config id: 335Faithfully yours, nginx.

2 weeks, 4 days назад @ kaspersky.ru
Самое важное об октябрьских патчах от Microsoft | Блог Касперского

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: bf1172655ea8738416272c1b910c4a23Server IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-10-14T17:00:37+03:00Config id: 335Faithfully yours, nginx.

2 weeks, 5 days назад @ kaspersky.ru
InjectEave: атака, позволяющая перехватить аналоговый аудиосигнал

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: 8c474b40de23335e23a81b4f71096fa2Server IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-10-13T18:00:32+03:00Config id: 335Faithfully yours, nginx.

2 weeks, 6 days назад @ kaspersky.ru
Вымогатели меняют тактику: кража данных вместо шифрования

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: 986285ee7f9fbca30f009118870a630eServer IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-10-09T19:00:10+03:00Config id: 335Faithfully yours, nginx.

3 weeks, 3 days назад @ kaspersky.ru
Как найти пропавшего питомца с помощью технологий | Блог Касперского

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: 61f641b9443f60bfa61c035e9925aff2Server IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-10-08T19:00:43+03:00Config id: 335Faithfully yours, nginx.

3 weeks, 4 days назад @ kaspersky.ru
Токеномика ИБ: атаки Denial of Wallet и стоимость работы SOC | Блог Касперского

An error occurred.

Sorry, the page you are looking for is currently unavailable.

Please try again later.

If you are the system administrator of this resource then you should check the error log for details.

Request id: db7c9e9b3ec5fc4fb9e02c8670f482a9Server IP: 185.54.220.248Client IP: 23.88.109.5Time: 2026-10-07T23:00:38+03:00Config id: 335Faithfully yours, nginx.

3 weeks, 5 days назад @ kaspersky.ru
Блог Group-IB
последний пост None
Cisco Security Blog Cisco Security Blog
последний пост 4 часа назад
Cisco AI Transit connects AI environments to your SD-WAN
Cisco AI Transit connects AI environments to your SD-WAN Cisco AI Transit connects AI environments to your SD-WAN

AI Transit connects specialized AI environments to the SD-WAN fabricThat customer requirement is what Cisco AI Transit is designed to address.

Connecting AI environments with Cisco AI TransitWhat is Cisco AI Transit?

Cisco AI Transit is designed to connect specialized AI environments to an enterprise’s existing Cisco SD-WAN fabric.

AI Transit builds on that foundation to connect specialized AI environments, including NeoClouds, private and sovereign AI clouds, and enterprise AI factories.

AI Transit is designed to connect workloads in NeoClouds, private and sovereign AI clouds, and enterprise AI factories to an existing Cisco SD-WAN fabric.

4 часа назад @ blogs.cisco.com
Defenders need more time to patch with the influx of patching hitting operations
Defenders need more time to patch with the influx of patching hitting operations Defenders need more time to patch with the influx of patching hitting operations

The velocity of vulnerabilities being discovered using Frontier AI and OpenWeight models such as Cisco Anteras is unprecedented and defenders need more time.

Virtual Patching vs. Live Protect (Shielding)Live Protect is a differentiating capability – we are not built the same.

The workload in the environment still sits vulnerable and that’s where Secure Workload can be expanded to drive controls based on CVE directly in the workload using native capabilities and once patched the control disappears.

Shielding with Live ProtectShielding with Live Protect is different.

Live Protect buys you time on the infrastructure boxes themselves without forcing an emergency upgrade window.

5 days, 5 hours назад @ blogs.cisco.com
Cisco Rethinks Privileged Infrastructure Access
Cisco Rethinks Privileged Infrastructure Access Cisco Rethinks Privileged Infrastructure Access

Infrastructure access has an identity problemPicture an infrastructure administrator pushing a configuration update across hundreds of switches during a maintenance window.

Introducing Cisco Privileged Infrastructure AccessToday, Cisco is introducing Privileged Infrastructure Access, a faster, more secure way to keep the network moving by enabling network administrators and agents to perform critical work through a secure, identity-bound connection.

For customers using Cisco ISE and TACACS+, Privileged Infrastructure Access can draw on the policy and device context they already manage to govern access to Cisco routers and switches.

That brings Cisco network context into the privileged acces…

1 week назад @ blogs.cisco.com
Unified Defense from Endpoint to Cloud: Real-Time Protection with Cisco Security, Splunk, and SentinelOne
Unified Defense from Endpoint to Cloud: Real-Time Protection with Cisco Security, Splunk, and SentinelOne Unified Defense from Endpoint to Cloud: Real-Time Protection with Cisco Security, Splunk, and SentinelOne

The data bears this out: in Splunk’s State of Security 2025 report, 78% of respondents said their security tools are dispersed and disconnected.

Closing that gap takes integrated identity, network, and endpoint context, plus the ability to act on it automatically.

That’s the idea behind combining SentinelOne’s runtime protection with Cisco Security and Splunk.

SentinelOne Runtime Protection and CWP in ActionSentinelOne Cloud Workload Protection (CWP) delivers autonomous, real-time threat detection and response across containers, Kubernetes, virtual machines, and serverless workloads.

Cisco Security extends that protection across identity, network, and perimeter, and Splunk gives your SOC on…

1 week, 4 days назад @ blogs.cisco.com
Cryptography Rarely Fails Because of the Math
Cryptography Rarely Fails Because of the Math Cryptography Rarely Fails Because of the Math

Upstream capacity: the projects you depend on can deliver new capabilities and critical fixes fast.

Upstream capacity is the one almost nobody puts on a roadmap because it sits outside your organization.

In most organizations, upstream capacity has none of those.

What This Looks Like in PracticeFor Cisco, part of the answer was becoming a Premier Sponsor of the OpenSSL Foundation in August 2025.

Tomáš Mráz, CTO of the OpenSSL Foundation, describes the impact:“Cisco’s support for the OpenSSL Foundation allowed us to fund an additional senior software engineer to improve the OpenSSL Library code.

2 weeks, 5 days назад @ blogs.cisco.com
Always-On Assurance: How Cisco is Reimagining the Secure Development Lifecycle
Always-On Assurance: How Cisco is Reimagining the Secure Development Lifecycle Always-On Assurance: How Cisco is Reimagining the Secure Development Lifecycle

CSDL continues, and does moreThe Cisco Secure Development Lifecycle (CSDL) is built on more than 400 software security requirements that validate products before they are released, with engagements at key stages of development.

Cisco open-sourced it and donated it to the Coalition for Secure AI (CoSAI).

Our secure software guidance skill is in development, carrying Cisco-specific security requirements into the development workflow.

Project CodeGuard and the secure software guidance skill also act as evaluators in the development pipeline, backing hard gates.

To date we have not found a novel issue that was not already covered by an existing software security requirement.

2 weeks, 6 days назад @ blogs.cisco.com
Chasing AMMYY at Splunk .conf
Chasing AMMYY at Splunk .conf Chasing AMMYY at Splunk .conf

The Splunk .conf network brought a new detection that we hadn’t seen before: Flawed AMMYY.

There is also a Remote Access Tool (RAT) called Flawed AMMYY that was developed from leaked AMMYY source code, and is directly used as malware.

One of the key value propositions of EVE is that it can use granular session fingerprinting to differentiate between similar but distinct applications like AMMYY and Flawed AMMYY.

Let’s dig into the events we saw for Flawed AMMYY and some of the details that EVE had to look at.

Our EVE detections for Flawed AMMYY came in pairs with identical timestamps, as seen above, all from a single IP.

3 weeks, 4 days назад @ blogs.cisco.com
Admin in the Loop: Firewalls and the Agentic SOC
Admin in the Loop: Firewalls and the Agentic SOC Admin in the Loop: Firewalls and the Agentic SOC

The event Network Operations Center (NOC) managed the venue network, providing our SOC firewalls with dedicated SPAN feeds directly from their core switches.

Inside Cisco Cloud Control, that story comes together in Unified Events.

While Splunk drives active investigations in the SOC, administrators maintain firewall health directly within Cloud Control.

The Horizon: Cisco Cloud Control & AI CanvasSecurity is now natively built into Cisco Cloud Control, the unified operations platform that brings Networking, Security, Observability, and Cloud into one consistent environment.

Without replacing individual product controllers, Cisco Cloud Control unifies inventory, topology, actions, identity, …

3 weeks, 4 days назад @ blogs.cisco.com
The Zero-Day Blind Spot: Why Your Agentic SOC needs Retrospective Packet Replay
The Zero-Day Blind Spot: Why Your Agentic SOC needs Retrospective Packet Replay The Zero-Day Blind Spot: Why Your Agentic SOC needs Retrospective Packet Replay

However, assessing whether a zero-day vulnerability was exploited in the past essentially involves going back in time.

Relying on standard logs or “Conditional / Selective PCAP” systems during a zero-day investigation leaves the Security Operations Center (SOC) team blind.

There is also a secondary benefit: if a breach occurred using an newly disclosed zero-day vulnerability, the attacker is likely to have been very sophisticated.

Replay The Relevant Historical Traffic Against The New Intrusion RulesOn the Firewall Threat Defense (FTD), we configured a dedicated interface for the Endace traffic replays.

Rapid retrospective packet replay transforms zero-day triage by delivering direct forens…

3 weeks, 4 days назад @ blogs.cisco.com
One Cisco in Action: Inside the Agentic SOC at .conf26
One Cisco in Action: Inside the Agentic SOC at .conf26 One Cisco in Action: Inside the Agentic SOC at .conf26

The .conf26 Agentic SOC was not a simulated demo or a scripted lab.

Powered by the Cisco Cloud Control management platform, Splunk Enterprise Security (ES), Cisco Security telemetry, Cisco Talos Intelligence, and Endace continuous packet capture, our joint team of Cisco, Splunk, Endace, and Jamf engineers demonstrated what multi-agent threat detection, investigation, and response (TDIR) delivers at enterprise scale.

Watch it come to life in David Bombal’s Interview at the Agentic SOC.

“The Agentic SOC is not about replacing human defenders with autonomous black boxes.

AcknowledgementsOur thanks to the engineers who built the Agentic SOC and the Humans who provided decision making expertise.

3 weeks, 4 days назад @ blogs.cisco.com
Splunk .conf26: Tracking the Triage Agent in the Agentic SOC
Splunk .conf26: Tracking the Triage Agent in the Agentic SOC Splunk .conf26: Tracking the Triage Agent in the Agentic SOC

Splunk .conf26 gave us the opportunity to operate a live Agentic Security Operations Center (SOC) in the middle of the Splunk community.

Splunk ES as the SOC data platformSplunk ES served as the primary analyst workspace and evidence system for the SOC.

Building the Triage Agent Dashboard in an AfternoonOnce the data was flowing and the agent was active, we built an operations dashboard in an afternoon.

The team preserved a path from telemetry to finding, from finding to agent analysis, and from agent analysis to an analyst decision.

Dashboard SnapshotThe following values are a snapshot from the displayed Triage Agent operations dashboard and should be read as event-environment observations…

3 weeks, 4 days назад @ blogs.cisco.com
Beyond the Box: Future-Proofing Branch Firewall Security for the AI Era
Beyond the Box: Future-Proofing Branch Firewall Security for the AI Era Beyond the Box: Future-Proofing Branch Firewall Security for the AI Era

The Cisco Secure Firewall 200 Series brings enterprise-grade protection and connectivity to distributed branches in a compact form factor.

The Encrypted Visibility Engine (EVE) uses AI and machine learning to analyze encrypted traffic, including TLS 1.3, without requiring full decryption.

The Secure Firewall 220 model delivers up to 1.5 Gbps of throughput with next-generation firewall capabilities enabled in a compact form factor for smaller branches.

The Secure Firewall 200 Series helps meet these demands with intelligent threat protection, encrypted traffic visibility, resilient connectivity, and centralized management.

Explore the Secure Firewall 200 Series to build a more resilient, man…

1 month назад @ blogs.cisco.com
From Love Letters to AI Agents: Cybersecurity’s Evolution
From Love Letters to AI Agents: Cybersecurity’s Evolution From Love Letters to AI Agents: Cybersecurity’s Evolution

Architecting the Future: The Four Pillars of Agentic SecuritySecuring agentic AI requires a new strategic framework.

Pillar 2: Core ProtectionDelivered by: Cisco AI DefenseCisco AI Defense provides specialized protection for the AI models themselves and their operational environment.

AI Inventory & Validation: This solution catalogs all deployed AI models and continuously validates their integrity against supply chain risks.

Pillar 4: ObservabilityDelivered by: SplunkSplunk provides the unified intelligence platform required to monitor and respond to agentic AI at scale.

Splunk ingests logs, events, and telemetry from Duo, Secure Access, AI Defense, and other infrastructure points, creating…

1 month, 1 week назад @ blogs.cisco.com
Black Hat USA 2026: Building the Agentic SOC, One Live Event at a Time
Black Hat USA 2026: Building the Agentic SOC, One Live Event at a Time Black Hat USA 2026: Building the Agentic SOC, One Live Event at a Time

Cisco was proud to return to Black Hat USA as the Official Security Cloud Provider and the longest-standing partner of the Black Hat Network Operations Center (NOC) and Security Operations Center (SOC).

In 2026, we completed our 11th year helping protect the Black Hat network, working side by side with the Black Hat NOC leaders and official technology partners: Palo Alto Networks, Arista, Corelight, Jamf and Lumen.

For Black Hat USA 2026, the Cisco and Splunk team brought together telemetry and workflows across Cisco Security, Splunk Security, and partner-provided network and security controls.

The same signal may need to be understood by Cisco, Splunk, Black Hat leadership, and partner tea…

1 month, 3 weeks назад @ blogs.cisco.com
Thrown into the SOC: A Black Hat First-Timer’s Story
Thrown into the SOC: A Black Hat First-Timer’s Story Thrown into the SOC: A Black Hat First-Timer’s Story

I did not walk into Black Hat with years of incident-response experience or an encyclopedic knowledge of threat actors.

The first time I walked into the Black Hat NOC, where the SOC team was operating, was a few days before the event began.

I was surrounded by people with years—sometimes decades—of experience, many of whom had supported Black Hat for years.

Check out the other blogs from our team at Black Hat USA 2026.

Driven by the needs of the community, Black Hat events showcase content directly from the community through Briefings presentations, Trainings courses, Summits, and more.

1 month, 3 weeks назад @ blogs.cisco.com
Microsoft Security Microsoft Security
последний пост 2 days, 19 hours назад
Inside a malicious Claude Code-branded extension and its persistent SSH backdoor
Inside a malicious Claude Code-branded extension and its persistent SSH backdoor Inside a malicious Claude Code-branded extension and its persistent SSH backdoor

It then attempts to install an SSH key, enable SSH, create a reverse tunnel, and configure persistence.

All applicable platforms: Stop confirmed malicious SSH and retry processes and remove their temporary .stk_ identity files after collection.

Follow-up Investigation and recoveryReview telemetry after the extension loaded for SSH key acceptance, tunnel processes, local SSH sessions, command execution, and file activity.

Microsoft Defender XDR detectionsMicrosoft Defender XDR customers can refer to the list of applicable detections below.

Tactic Observed activity Microsoft Defender coverage Execution Execution of suspicious shell scripts to support backdoor activity.

2 days, 19 hours назад @ microsoft.com
From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths
From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths

Both incidents followed a shared entry and execution pattern before diverging into two AD CS abuse paths.

Host discovery and AD CS assessmentThe staged components queried Windows version information, network configuration, and running processes.

Case 2: Help desk impersonation led to PetitPotam authentication coercion, ESC8 relay to AD CS, certificate-based Kerberos authentication, and customer-led device isolation.

NTLM relay reaches AD CS Web EnrollmentThe attacker relayed the domain controller’s NTLM authentication to AD CS Web Enrollment.

Search for Teams support impersonation, portable Bun or Java runtimes, AD CS certificate abuse, NTLM relay, ESC1, ESC8, and certificate-based Kerberos…

3 days, 4 hours назад @ microsoft.com
Tracking AI adoption in North Korean threat actor tradecraft
Tracking AI adoption in North Korean threat actor tradecraft Tracking AI adoption in North Korean threat actor tradecraft

Microsoft Threat Intelligence assesses the overall adoption of AI across North Korean threat actors as high, with threat actors such as Jade Sleet, Coral Sleet, and Jasper Sleet demonstrating an established use of AI across all operational workflows, alongside increasing adoption across the broader North Korean threat actor set.

This blog breaks down how North Korean threat actors are utilizing AI across their operations, reflecting a broader trend of threat actors incorporating AI into their attack chains.

Stages of AI adoption by North Korean threat actorsNorth Korean threat actors are increasingly integrating generative and agentic AI platforms into their operations, but the rate and mat…

4 days, 4 hours назад @ microsoft.com
IDC MarketScape names Microsoft a Leader in the 2026 Worldwide Modern Endpoint Security for Enterprises Vendor Assessment
IDC MarketScape names Microsoft a Leader in the 2026 Worldwide Modern Endpoint Security for Enterprises Vendor Assessment IDC MarketScape names Microsoft a Leader in the 2026 Worldwide Modern Endpoint Security for Enterprises Vendor Assessment

Today, we’re proud to share thatMicrosoft has been named a Leader in the 2026 IDC MarketScape for Worldwide Modern Endpoint Security for Enterprises (Doc #US54123526, September 2026).

On top of that foundation, we continue to strengthen what Defender can see:Richer endpoint signals: Defender provides more than 200 native event types for threat hunting.

Microsoft named a Leader by IDC Read the 2026 IDC MarketScape to learn why IDC named Microsoft a Leader in Worldwide Modern Endpoint Security for Enterprises.

Read the reportTo learn more about Microsoft Security solutions, visit our website.

Follow us on LinkedIn (Microsoft Security) and X (@MSFTSecurity) for the latest news and updates on c…

4 days, 4 hours назад @ microsoft.com
The CISO’s evolving role: Protecting and defending in the agentic era
The CISO’s evolving role: Protecting and defending in the agentic era The CISO’s evolving role: Protecting and defending in the agentic era

And we have to rethink how we defend that enterprise as attackers use AI to move faster and operate at greater scale.

For CISOs: Defending differentlyYour second job is to defend differently than you have historically done.

The same capabilities that make attacks faster can make defense faster, with agents working alongside your analysts to investigate and respond.

Prepare for an agent-driven workplace Explore Work Trend Index insights on the changing role of agents at work and the trends shaping how organizations operate.

Explore the Work Trend IndexIf you’re building with AI, bring your security team in early and have the identity and data conversation.

5 days, 4 hours назад @ microsoft.com
Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks
Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks Inside the LiteLLM 1.107.0 supply chain compromise: Credential theft through Python startup hooks

Compromised package distributionThe compromised LiteLLM 1.107.0 release delivered malicious Python startup files to environments where the package was installed.

Onboard supported developer workstations, build agents, and AI gateway servers to Microsoft Defender for Endpoint, and enable Microsoft Defender Antivirus real-time and cloud-delivered protection where supported.

Microsoft Defender XDR detectionsAs of October 22, 2026, the following Microsoft Defender Antivirus signatures and Microsoft Defender for Endpoint alerts were available for activity associated with the compromised LiteLLM 1.107.0 release.

Microsoft Defender XDR Threat analyticsInside the LiteLLM 1.107.0 supply chain compro…

1 week, 3 days назад @ microsoft.com
AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise
AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise

Microsoft Defender XDR provides detections and hunting queries for suspicious Microsoft Graph activity and activity associated with known threat infrastructure.

Microsoft Threat Intelligence has identified threat actors across multiple geographic regions leveraging the ARTEX framework.

Preserve available Microsoft Entra sign-in and audit records, Microsoft Purview Audit records, SIEM data, and previously configured Microsoft Graph telemetry.

Suspicious sign-in from verified nation-state threat actor infrastructure Steal Application Access TokenA sign-in was observed from a known threat actor IP address.

We recommend promptly investigating this alert, as a threat actor might already be using…

1 week, 5 days назад @ microsoft.com
Agents are your newest insiders. Security must move at their speed.
Agents are your newest insiders. Security must move at their speed. Agents are your newest insiders. Security must move at their speed.

Guardian Agents help security teams operate continuously, at machine speed and scale, while sensors, context, and actuators across the cyber stack help understand changing agent risk and continuously adapt protection in response.

Dynamic Agent RiskDynamic Agent Risk combines signals from identity, data, endpoints, cloud, network, runtime, and the agent’s own activity.

Guardian Agents carry out the work at machine speed, adapting as agent activity, risk, security context, and organizational policy change.

To learn more about Microsoft Security solutions, visit our website.

Also, follow us on LinkedIn (Microsoft Security) and X (@MSFTSecurity) for the latest news and updates on cybersecurity.

2 weeks назад @ microsoft.com
Managing open-weight model risk in enterprise deployments
Managing open-weight model risk in enterprise deployments Managing open-weight model risk in enterprise deployments

As enterprises choose which models to deploy, the relevant question is broader than whether a model is open-weight or closed-weight.

Today, Microsoft and NVIDIA are publishing Risk Management for Open-Weight Models in Enterprise, the first in a planned series of joint resources intended to help enterprises address those questions.

Model access and deployment are separate choices: open-weight models can also be used through managed platforms.

Building on this workRisk Management for Open-Weight Models in Enterprise focuses primarily on the model layer.

Read the joint Microsoft-NVIDIA paper, Risk Management for Open-Weight Models in Enterprise.

2 weeks, 3 days назад @ microsoft.com
The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime
The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime The hidden network: Inside the phishing infrastructure ecosystem powering global cybercrime

Microsoft’s research into one phishing kit unraveled a larger ecosystem, including the phishing kit developers, an infrastructure dealer, and the threat actors who buy from both.

Downstream activity from Storm-2990 phishing kitsMicrosoft observed downstream activity by threat actors using infrastructure affiliated with the Storm-2990 phishing kits.

Most of the activity that stems from this phishing kit ecosystem consists of social engineering, phishing operations, and account and storage takeovers.

ReferencesLearn moreFor the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog.

To hear stories and insights from the Micr…

2 weeks, 5 days назад @ microsoft.com
Post-quantum authentication: Why organizations should start testing certificate ecosystems now
Post-quantum authentication: Why organizations should start testing certificate ecosystems now Post-quantum authentication: Why organizations should start testing certificate ecosystems now

Early testing can surface compatibility and process gaps before post-quantum authentication is required at scale.

As the industry moves toward post-quantum authentication, security teams will need greater visibility into those dependencies.

Why organizations should begin preparing nowThe transition to post-quantum authentication is unlikely to be a single technology upgrade.

Testing the future certificate ecosystemTo help the ecosystem gain practical experience with post-quantum authentication, Microsoft launched the PQC TLS Pilot Program on August 27, 2026.

What organizations can do todayOrganizations do not need to wait for broad industry adoption to begin preparing for post-quantum authe…

3 weeks, 3 days назад @ microsoft.com
3 lessons from frontier AI vulnerability research
3 lessons from frontier AI vulnerability research 3 lessons from frontier AI vulnerability research

The mission of Microsoft Security’s Frontier Offensive Research & Generative Exploitation (FORGE) Lab is to advance the frontier of autonomous security engineering.

We’re building a team that enables AI-native vulnerability research at Microsoft, pushing the boundaries of finding and fixing zero-day vulnerabilities.

Three lessons follow, each marking a shift in how we approach vulnerability research:From frontier capability to scale.

Here, we focus on what those experiences teach us about operating vulnerability research at scale—across Windows and open-source projects.

FORGE has submitted nine Linux findings with internally assessed common vulnerability scoring system (CVSS) scores above 7…

3 weeks, 5 days назад @ microsoft.com
CISO perspectives on managing vulnerability risks in the age of AI
CISO perspectives on managing vulnerability risks in the age of AI CISO perspectives on managing vulnerability risks in the age of AI

How do frontier AI models change vulnerability management for CISOs?

We use a ‘harness’ layer around AI models in vulnerability scanning for better results.

They should do so without delay, rather than wait for access to frontier AI models.

Extensive guidance can be found in a new Microsoft Security Exposure Management page with capabilities customers can use to act.

Final notesThe advent of frontier AI models to discover and exploit vulnerabilities creates both risks and opportunities.

3 weeks, 6 days назад @ microsoft.com
CISO perspectives on managing vulnerability risks in the age of AI
CISO perspectives on managing vulnerability risks in the age of AI CISO perspectives on managing vulnerability risks in the age of AI

How do frontier AI models change vulnerability management for CISOs?

We use a ‘harness’ layer around AI models in vulnerability scanning for better results.

They should do so without delay, rather than wait for access to frontier AI models.

Extensive guidance can be found in a new Microsoft Security Exposure Management page with capabilities customers can use to act.

Final notesThe advent of frontier AI models to discover and exploit vulnerabilities creates both risks and opportunities.

3 weeks, 6 days назад @ microsoft.com
Insights from the 2026 Microsoft Digital Defense Report
Insights from the 2026 Microsoft Digital Defense Report Insights from the 2026 Microsoft Digital Defense Report

Every year, the Microsoft Digital Defense Report gives us an opportunity to step back from individual threats and look broadly at what Microsoft’s security and threat intelligence teams are seeing.

These developments can change the speed and scale of security activity even as the underlying security fundamentals remain familiar.

People, identities, exposed systems, and trusted access continue to feature prominently in the threat activity Microsoft observes.

The 2026 Microsoft Digital Defense Report looks across the threat landscape, cybercrime, resilience, and the relationships among technologies, identities, systems, and people.

Read the 2026 Digital Defense Report for the full findings, d…

1 month назад @ microsoft.com
Google Online Security Blog Google Online Security Blog
последний пост 6 months, 1 week назад
AI threats in the wild: The current state of prompt injections on the web
AI threats in the wild: The current state of prompt injections on the web AI threats in the wild: The current state of prompt injections on the web

Here, threat actors may simply seed prompt injections on websites in hope of corrupting AI systems that browse them.

Early experiments revealed a significant volume of "benign" prompt injection text, which illustrates the complexity of distinguishing between functional threats and harmless content.

Many prompt injections were found in research papers, educational blog posts, or security articles discussing this very topic.

(Source: GitHub/swisskyrepo)When searching for prompt injections naively, the majority of detections are benign content – false positives in our case.

Malicious: ExfiltrationWe were able to observe a small number of prompt injections that aim at theft of data.

6 months, 1 week назад @ security.googleblog.com
Bringing Rust to the Pixel Baseband
Bringing Rust to the Pixel Baseband Bringing Rust to the Pixel Baseband

Recognizing the risks associated within the complex modem firmware, Pixel 9 shipped with mitigations against a range of memory-safety vulnerabilities.

Following our previous discussion on "Deploying Rust in Existing Firmware Codebases", this post shares a concrete application: integrating a memory-safe Rust DNS(Domain Name System) parser into the modem firmware.

Hook-up Rust to modem firmwareBefore building the Rust DNS library, we defined several Rust unit tests to cover basic arithmetic, dynamic allocations, and FFI to verify the integration of Rust with the existing modem firmware code base.

Pixel modem firmware already has a well-tested and specialized global memory allocation system to…

6 months, 3 weeks назад @ security.googleblog.com
Protecting Cookies with Device Bound Session Credentials
Protecting Cookies with Device Bound Session Credentials Protecting Cookies with Device Bound Session Credentials

This project represents a significant step forward in our ongoing efforts to combat session theft, which remains a prevalent threat in the modern security landscape.

Session theft typically occurs when a user inadvertently downloads malware onto their device.

Once active, the malware can silently extract existing session cookies from the browser or wait for the user to log in to new accounts, before exfiltrating these tokens to an attacker-controlled server.

How DBSC WorksDBSC protects against session theft by cryptographically binding authentication sessions to a specific device.

The issuance of new short-lived session cookies is contingent upon Chrome proving possession of the correspondi…

6 months, 3 weeks назад @ security.googleblog.com
Google Workspace’s continuous approach to mitigating indirect prompt injections
Google Workspace’s continuous approach to mitigating indirect prompt injections Google Workspace’s continuous approach to mitigating indirect prompt injections

Staying ahead of the latest indirect prompt injection attacks is critical to our mission of securing Workspace with Gemini.

In our previous blog “Mitigating prompt injection attacks with a layered defense strategy”, we reviewed the layered architecture of our IPI defenses.

Synthetic data generationAfter we discover, curate, and catalog new attacks, we use Simula to generate synthetic data expanding these new attacks.

We partition the synthetic data described above into separate training and validation sets to ensure performance is evaluated against held-out examples.

This process leverages the newly generated synthetic attack data described on this blog, to create a robust, end-to-end evalu…

7 months назад @ security.googleblog.com
VRP 2025 Year in Review
VRP 2025 Year in Review VRP 2025 Year in Review

2025 marked a special year in the history of vulnerability rewards and bug bounty programs at Google: our 15th anniversary 🎉🎉🎉!

Coming back to 2025 specifically, our VRP once again confirmed the ongoing value of engaging with the external security research community to make Google and its products safer.

Vulnerability Reward Program 2025 in NumbersWant to learn more about who’s reporting to the VRP?

Tip: Want to be informed of new developments and events around our Vulnerability Reward Program?

Follow the Google VRP channel on X to stay in the loop and be sure to check out the Security Engineering blog, which covers topics ranging from VRP updates to security practices and vulnerability des…

7 months назад @ security.googleblog.com
Security for the Quantum Era: Implementing Post-Quantum Cryptography in Android
Security for the Quantum Era: Implementing Post-Quantum Cryptography in Android Security for the Quantum Era: Implementing Post-Quantum Cryptography in Android

To stay ahead of the curve, the technology industry must undertake a proactive, multi-year migration to Post-Quantum Cryptography (PQC).

To bring these critical protections to the wider developer community with minimal friction, the transition will be supported through Play App Signing.

Play App Signing leverages Google Cloud KMS, which helps ensure industry-leading compliance standards, to secure signing keys.

Empower Developers : The inclusion of ML-DSA support within Android Keystore and Play App Signing allows developers to safeguard their users and application.

: The inclusion of ML-DSA support within Android Keystore and Play App Signing allows developers to safeguard their users and …

7 months, 1 week назад @ security.googleblog.com
Cultivating a robust and efficient quantum-safe HTTPS
Cultivating a robust and efficient quantum-safe HTTPS Cultivating a robust and efficient quantum-safe HTTPS

Today we're announcing a new program in Chrome to make HTTPS certificates secure against quantum computers.

Instead, Chrome, in collaboration with other partners, is developing an evolution of HTTPS certificates based on Merkle Tree Certificates (MTCs), currently in development in the PLANTS working group.

Since MTC technology shares significant architectural similarities with CT, these operators are uniquely qualified to ensure MTCs are able to get off the ground quickly and successfully.

The Chrome Quantum-resistant Root Program will operate alongside our existing Chrome Root Program to ensure a risk-managed transition that maintains the highest levels of security for all users.

First, we…

8 months, 1 week назад @ security.googleblog.com
Staying One Step Ahead: Strengthening Android’s Lead in Scam Protection
Staying One Step Ahead: Strengthening Android’s Lead in Scam Protection Staying One Step Ahead: Strengthening Android’s Lead in Scam Protection

For Majik, Scam Detection was the intervention he needed: “The warning is what made me pause and avoid a bad situation”.

As scammers evolve their tactics and create more convincing and personalized threats, we’re using the best of Google AI to stay one step ahead.

Expanding Scam Detection for Calls to Samsung DevicesTo help protect you during phone calls, Scam Detection alerts you if a caller uses speech patterns commonly associated with fraud.

Scam Detection for phone calls on Google Pixel devices is available in the U.S., Australia, Canada, India, Ireland, and the UK.

Powered by Gemini’s on-device model, Scam Detection provides intelligent protection against scam calls while ensuring that…

8 months, 1 week назад @ security.googleblog.com
Keeping Google Play & Android app ecosystems safe in 2025
Keeping Google Play & Android app ecosystems safe in 2025 Keeping Google Play & Android app ecosystems safe in 2025

Upgrading Google Play’s AI-powered, multi-layered user protectionsWe’ve seen a clear impact from these safety efforts on Google Play.

As Android’s built-in defense against malware and unwanted software, Google Play Protect now scans over 350 billion Android apps daily.

This proactive protection constantly checks both Play apps and those from other sources to ensure they are not potentially harmful.

Looking aheadOur top priority remains making Google Play and Android the most trusted app ecosystems for everyone.

Thank you for being part of the Google Play and Android community as we work together to build a safer app ecosystem.

8 months, 2 weeks назад @ security.googleblog.com
New Android Theft Protection Feature Updates: Smarter, Stronger
New Android Theft Protection Feature Updates: Smarter, Stronger New Android Theft Protection Feature Updates: Smarter, Stronger

That’s why we're committed to providing multi-layered defenses that help protect you before, during, and after a theft attempt.

Today, we're announcing a powerful set of theft protection feature updates that build on our existing protections, designed to give you greater peace of mind by making your device a much harder target for criminals.

These updates are now available for Android devices running Android 16+.

More User Control for Failed Authentications: In Android 15, we launched Failed Authentication Lock, a feature that automatically locks the device's screen after excessive failed authentication attempts.

This feature is now getting a new dedicated enable/disable toggle in settings,…

9 months, 1 week назад @ security.googleblog.com